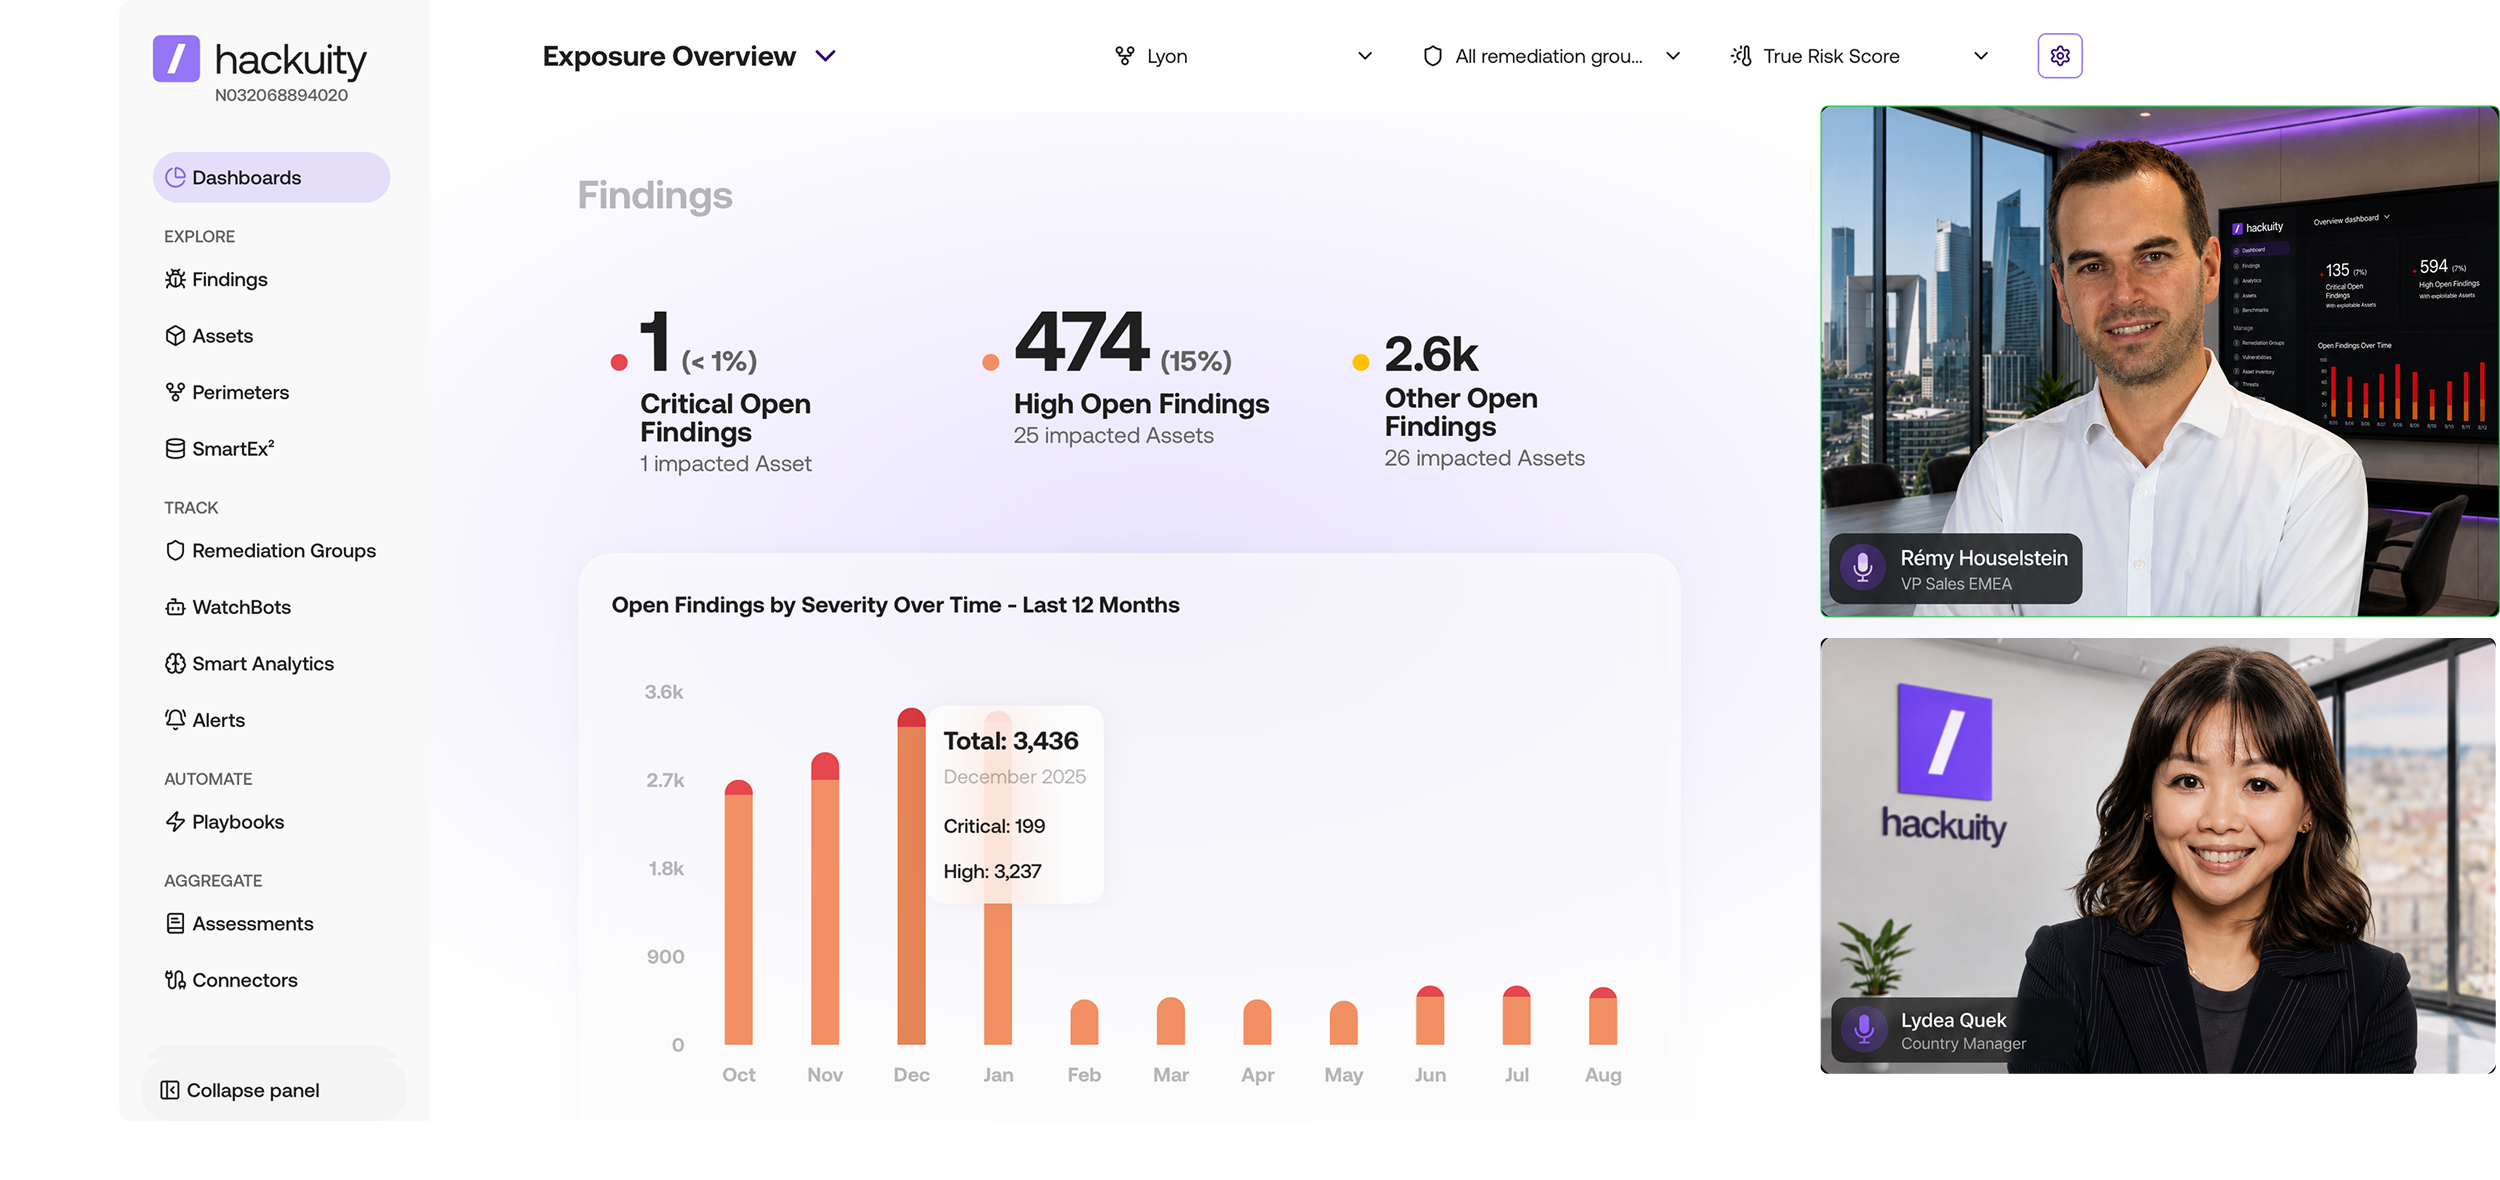









The launch is designed to help security teams prioritise vulnerabilities at a time when they must monitor and manage an ever-growing number of CVEs. In 2023 alone, more than 29,000 vulnerabilities were disclosed. With WatchBot, security teams can select the parameters through which to filter the alerts on vulnerabilities and retrieve only those matching their specific criteria and the technologies they manage. When a new CVE matches the monitored technologies and filters defined in the WatchBot, it is added to the current list of CVEs, enabling security teams to put remediation into action.
This empowers IT teams to manage their time and resources more effectively and to fix systems before attackers can exploit them. It provides instant alerts of vulnerabilities that normal scanning processes might miss and allows teams to focus only on the severe and exploitable vulnerabilities.
Key Features
Technology Filters
WatchBot fully automates the process of CVE monitoring based on technologies within an organisation’s IT estate, which can be defined by vendor, product, version, and more. Technologies can be monitored, and filters set, according to three different factors: ‘all versions’, ‘specific versions’, or ranges of technology versions.
CVE Filters
Any CVEs affecting these monitored technologies can be filtered using criteria including a Common Vulnerability Scoring System (CVSS) base score, exploitability, threat intensity, exploit maturity, the exploit prediction scoring system (EPSS), and CISA’s Known Exploited Vulnerabilities (KEV) Catalog.
Alerting Channels
Each time WatchBot identifies a new CVE that matches the criteria set, an alert is sent to a tailored distribution list via the user’s preferred channel such as email, Slack, or Teams.
Commenting on the launch, Sylvain Cortes, VP Strategy, Hackuity said:
“Security teams face a double jeopardy of challenges in prioritising vulnerabilities: their IT estates – and the attack surfaces – are growing and the number of threats is escalating. Scanning for vulnerabilities is vital, but it’s imperfect either because traditional scans are too slow, execution cycles are too far apart, or it’s simply not possible to scan a particular environment. And the fact is that only a small number of threats will contribute a high risk to an organisation.”
He continues:
“WatchBot closes these security gaps, automating and simplifying the process of CVE monitoring with a tailored alerting system which is unique to each organisation. This means teams can put a risk-based approach at the heart of their Vulnerability Operations Centre (VOC). As security teams are increasingly faced with doing more with less, this approach is more important than ever.”
WatchBot is available to all existing customers of Hackuity’s Risk-Based Vulnerability Management platform.
About Hackuity
80% of cyberattacks use a vulnerability published half a decade ago. Translation: either cybersec professionals don’t care (not true) or they can’t keep up on their own (it’s time we admit that). Fragmented teams, too many tools, and exploding vulnerabilities are a match made in heaven – for attackers.
Founded by experts from leading cybersecurity service providers, Hackuity reinvents Risk-Based Vulnerability Management (RBVM) to protect organisations worldwide:
- Aggregate 80+ market-leading tools into a single pane of glass.
- Prioritise vulnerabilities with our risk-based scoring algorithm.
- Automate remediation specific to your attack surface.
Integrate your ecosystem to help cybersec teams focus on what’s actually vulnerable – not on managing Excel spreadsheets. Hackuity’s platform breaks security silos and provides a unified view of your cyber exposure specific to your attack surface so that you can remediate the real threats, faster. In short, Hackuity is your VOC enabler.
Hackuity is the winner of PwC Luxembourg's Cybersecurity & Privacy Solution of the Year – People’s Choice Award (2023), has received the EIC Seal of Excellence from the European Innovation Counsel, and is featured on Wavestone’s 2023 French Cybersecurity Scaleups Radar. Hackuity is a member of Campus Cyber and has also won the Government-led Grand Défi competition (2023, 2021), the Assises Innovation Award (2021), the FIC Startup Jury Award (2021), and the BPI Innovation Competition Award (2019). SOC 2 Type II certified and IMDA accredited, Hackuity emerged from stealth and raised €12 million in 2022.


VR-1 | Property |
|---|---|
Model type | Post-trained cyber reasoning model |
Primary specialization | Multi-domain enterprise attack-chain discovery |
Starting condition | A scoped foothold and a concrete objective |
Operating surfaces | Cloud, identity, runtime, code, CI/CD, SaaS, and organizational context |
Success signal | Execution-verified completion of the objective |
Primary evaluation | IntrusionBench |
Preliminary result (preview) | More than 2× black-box pass@3 over the strongest evaluated frontier baseline |
Trajectory budget | Two-hour wall-clock limit per trajectory, or 250 agent turns (whichever comes first) |