From vulnerability overload to prioritized action.
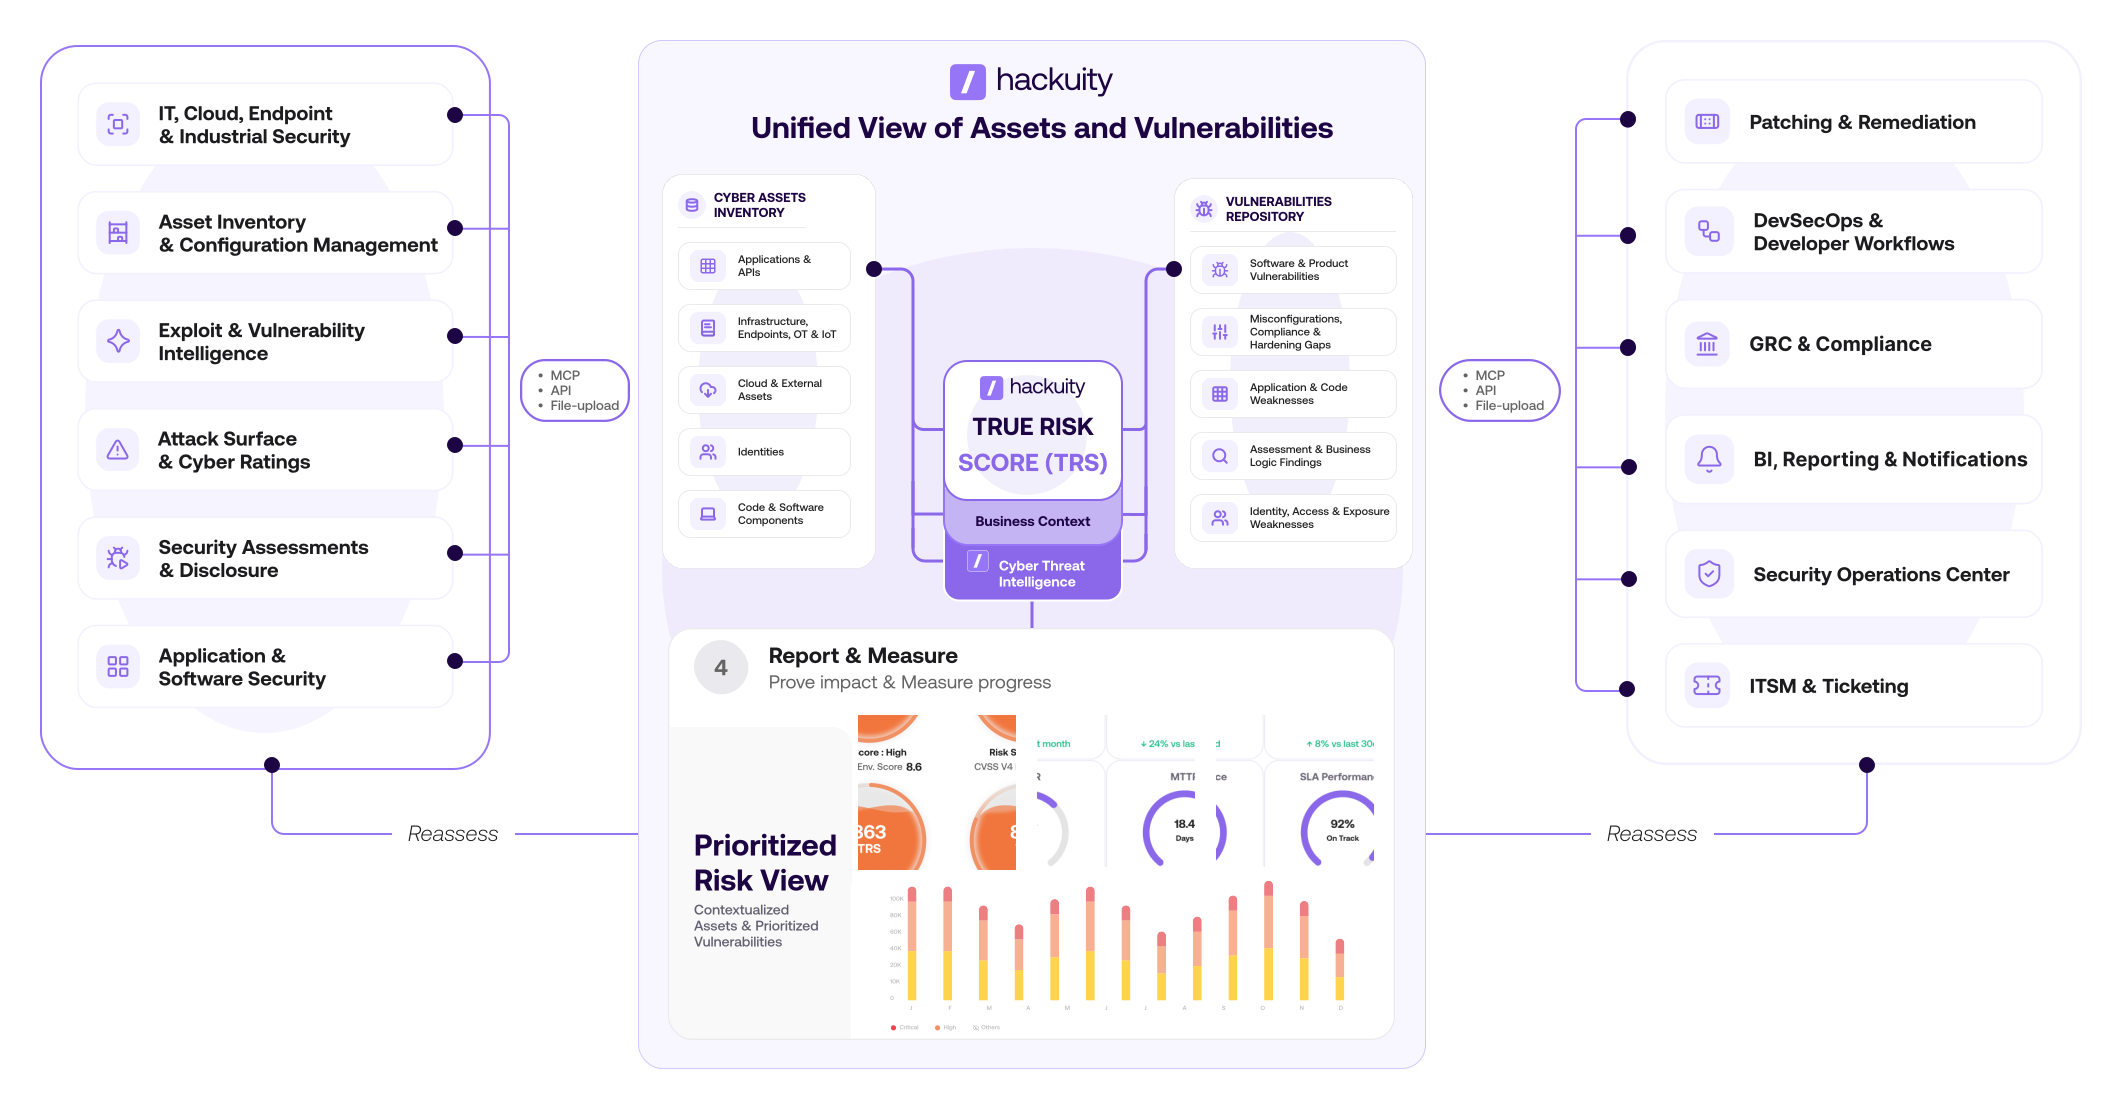
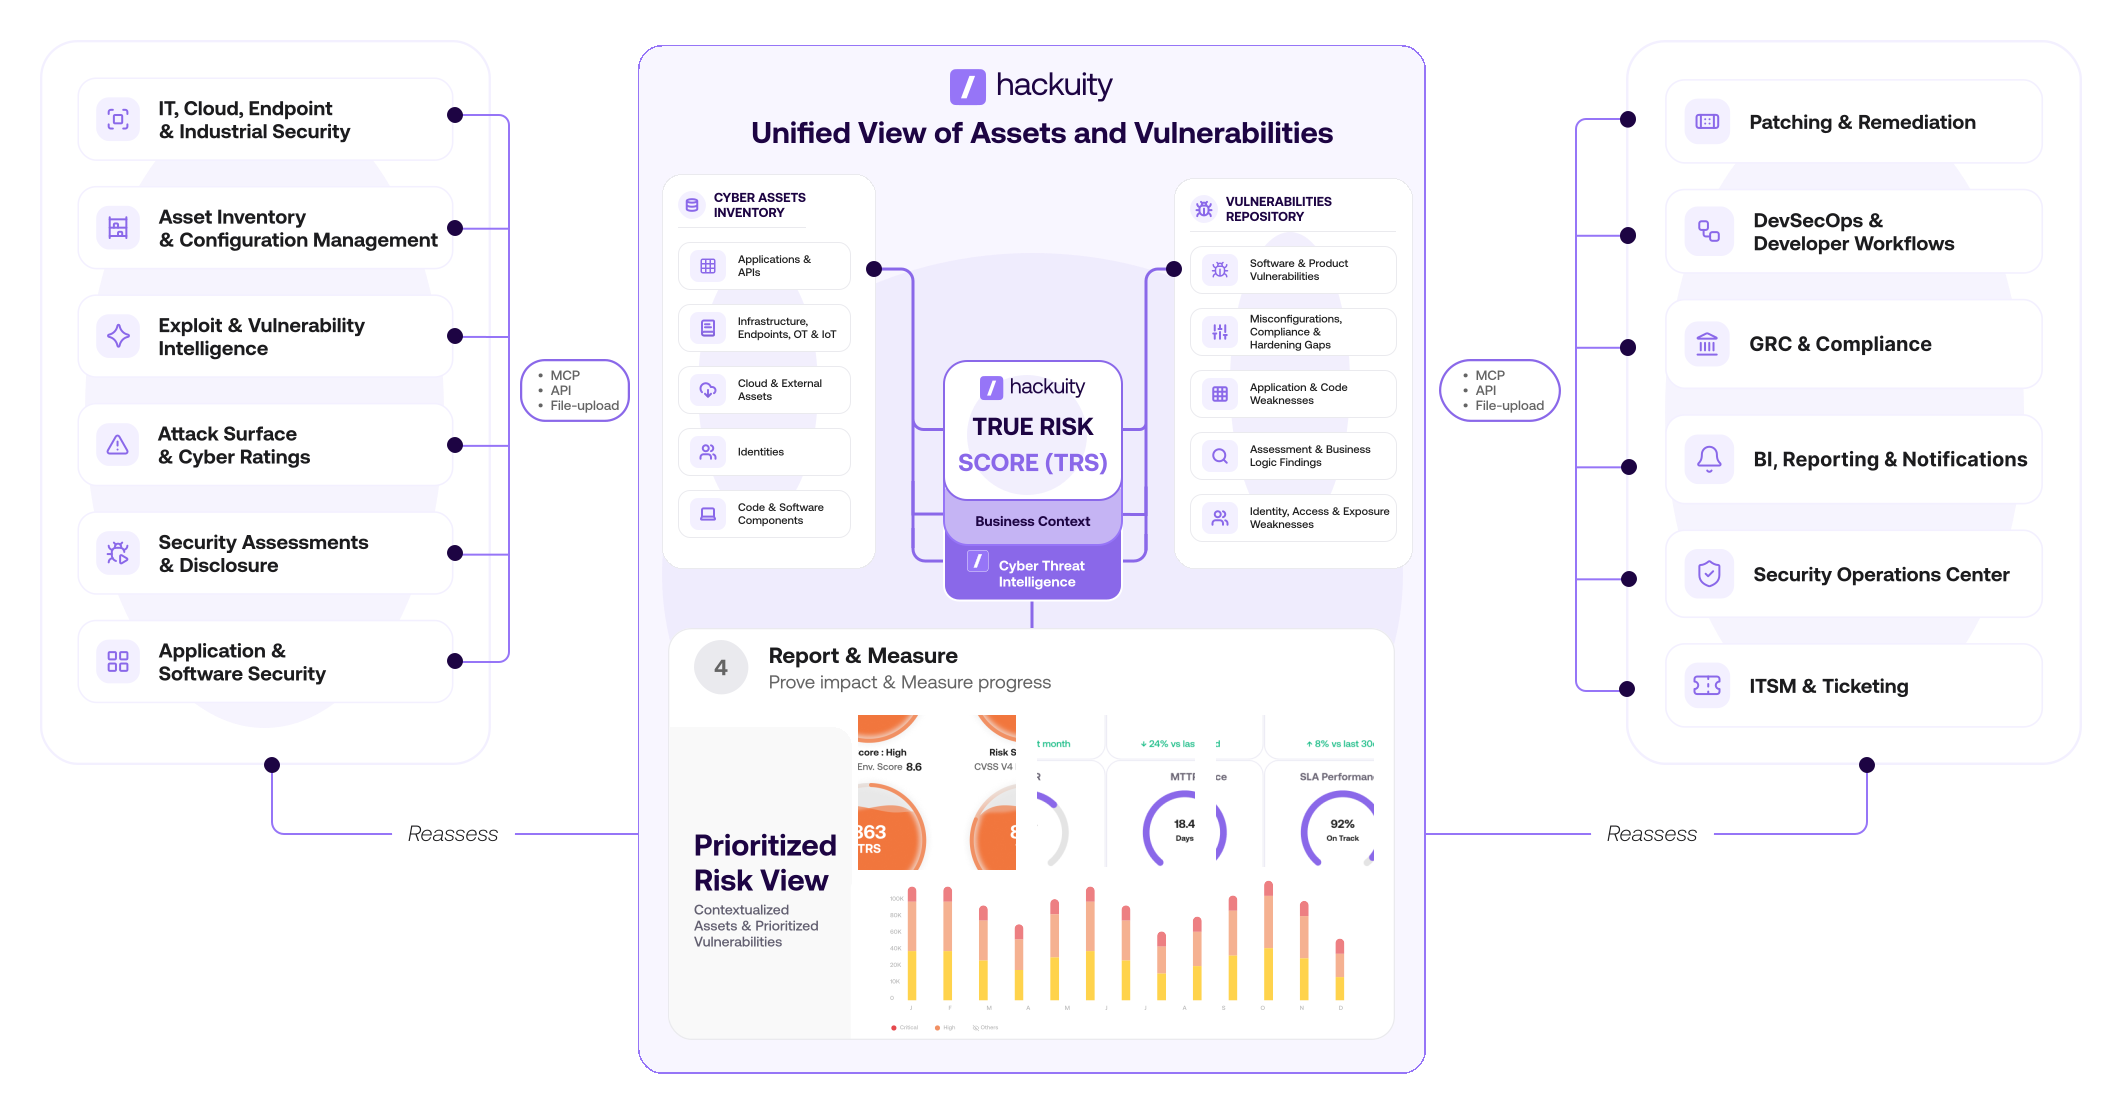
Hackuity consolidates findings and assets across your security stack, prioritizes what matters, and coordinates remediation, so your team spends less time managing security outputs and more time reducing risk.
0+
integrations
0+
Users connected
0M+
Assets managed
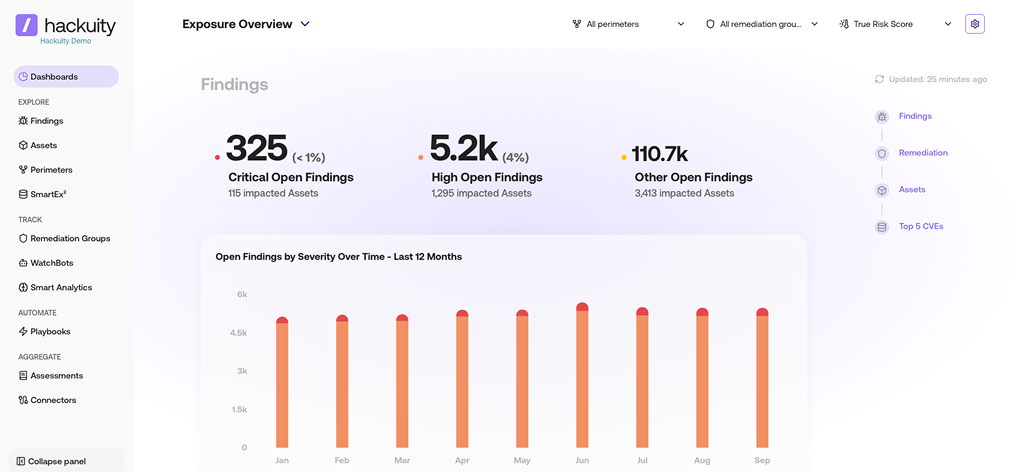
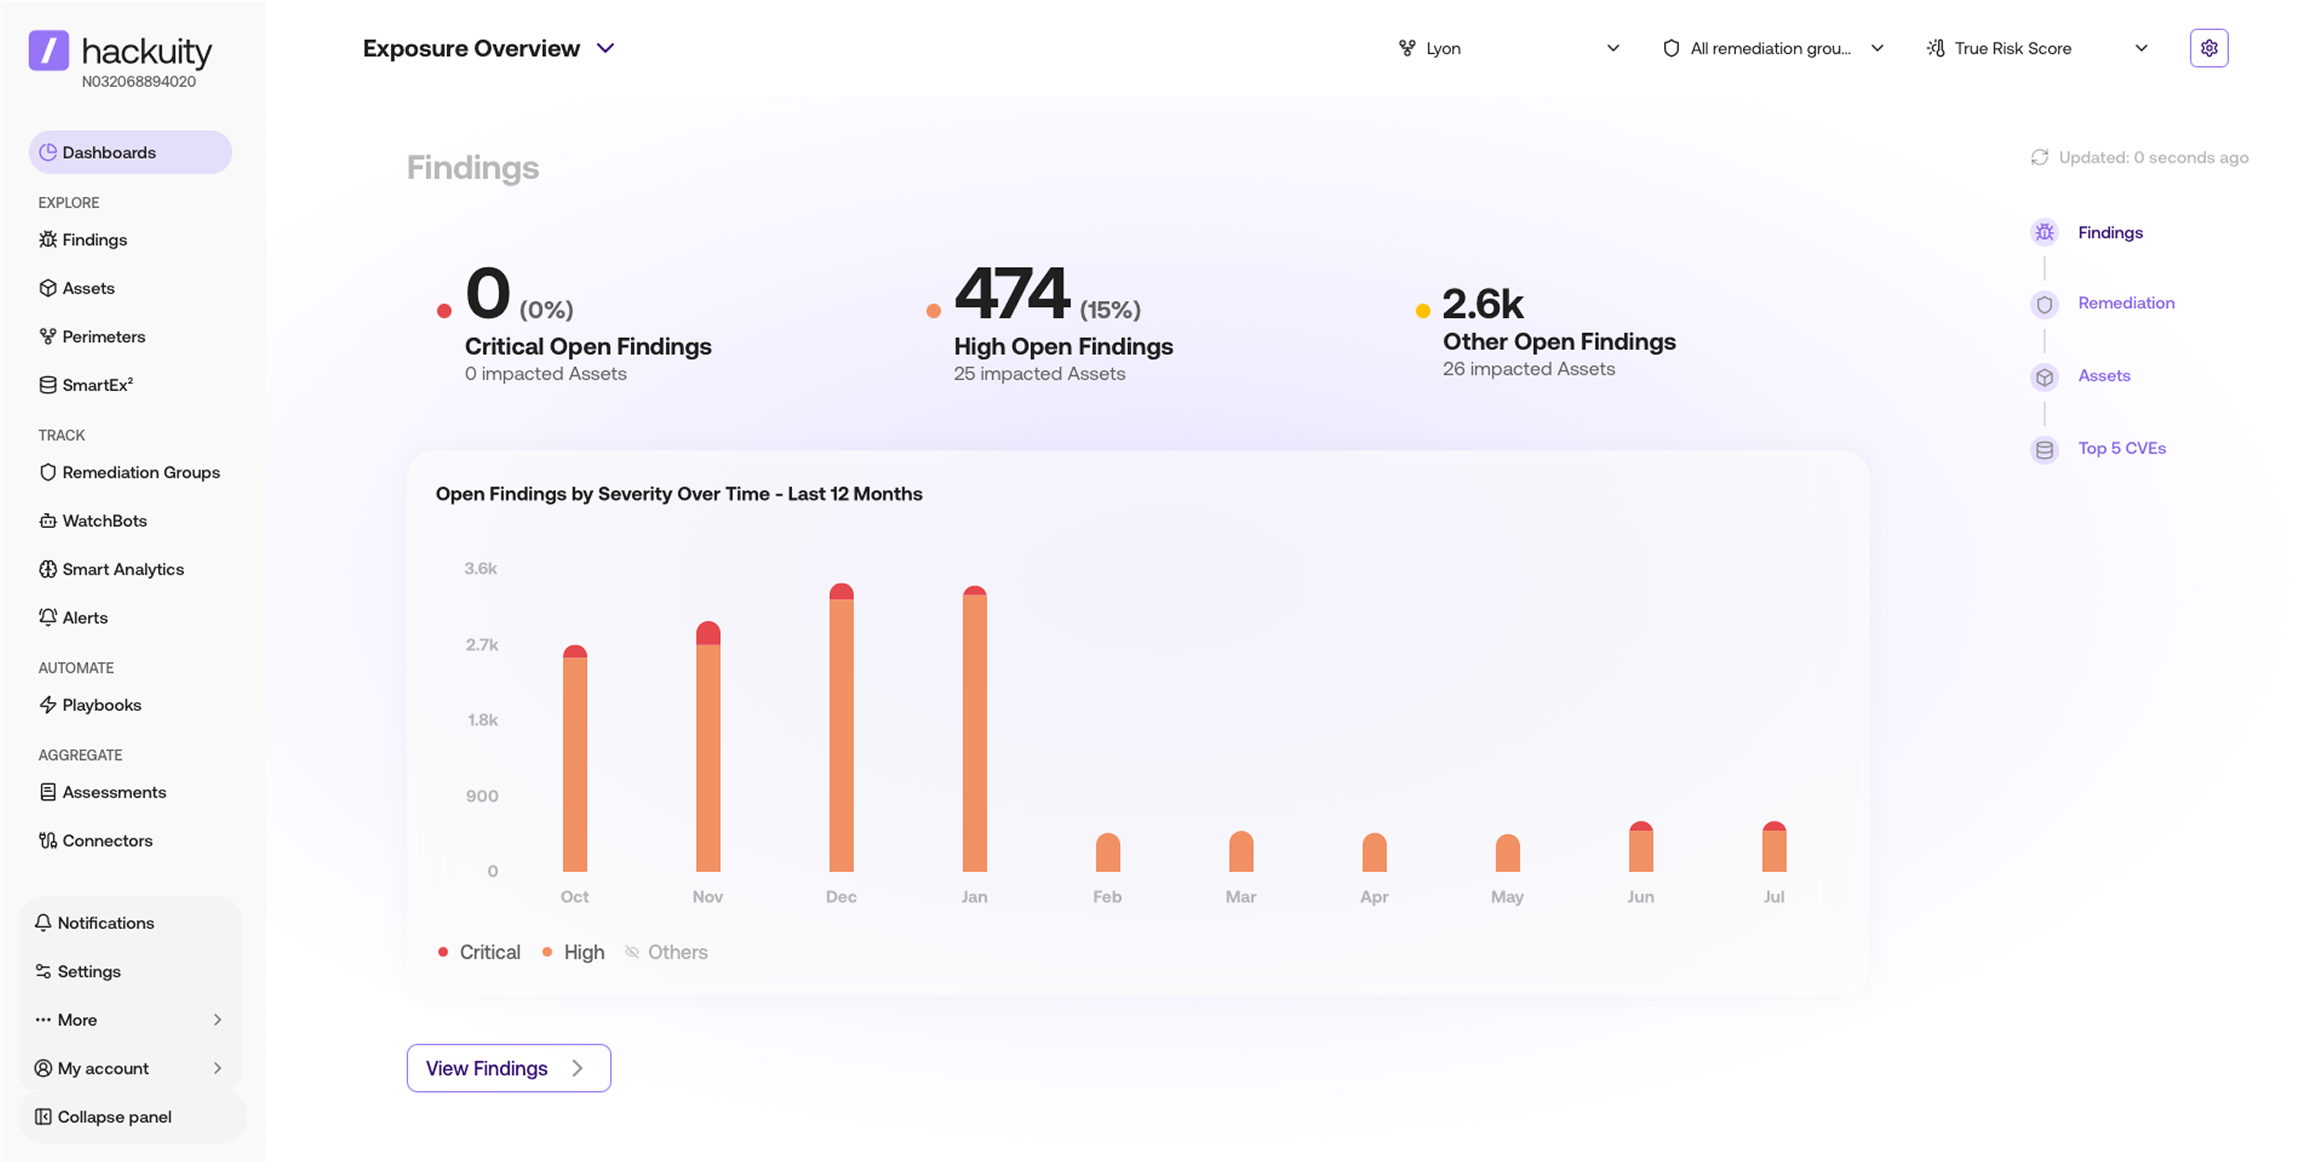
Screenshot of the Hackuity Exposure Overview dashboard showing the full navigation sidebar and 325 critical, 5.2k high, and 110.7k other open findings, with a 12-month bar chart of findings by severity

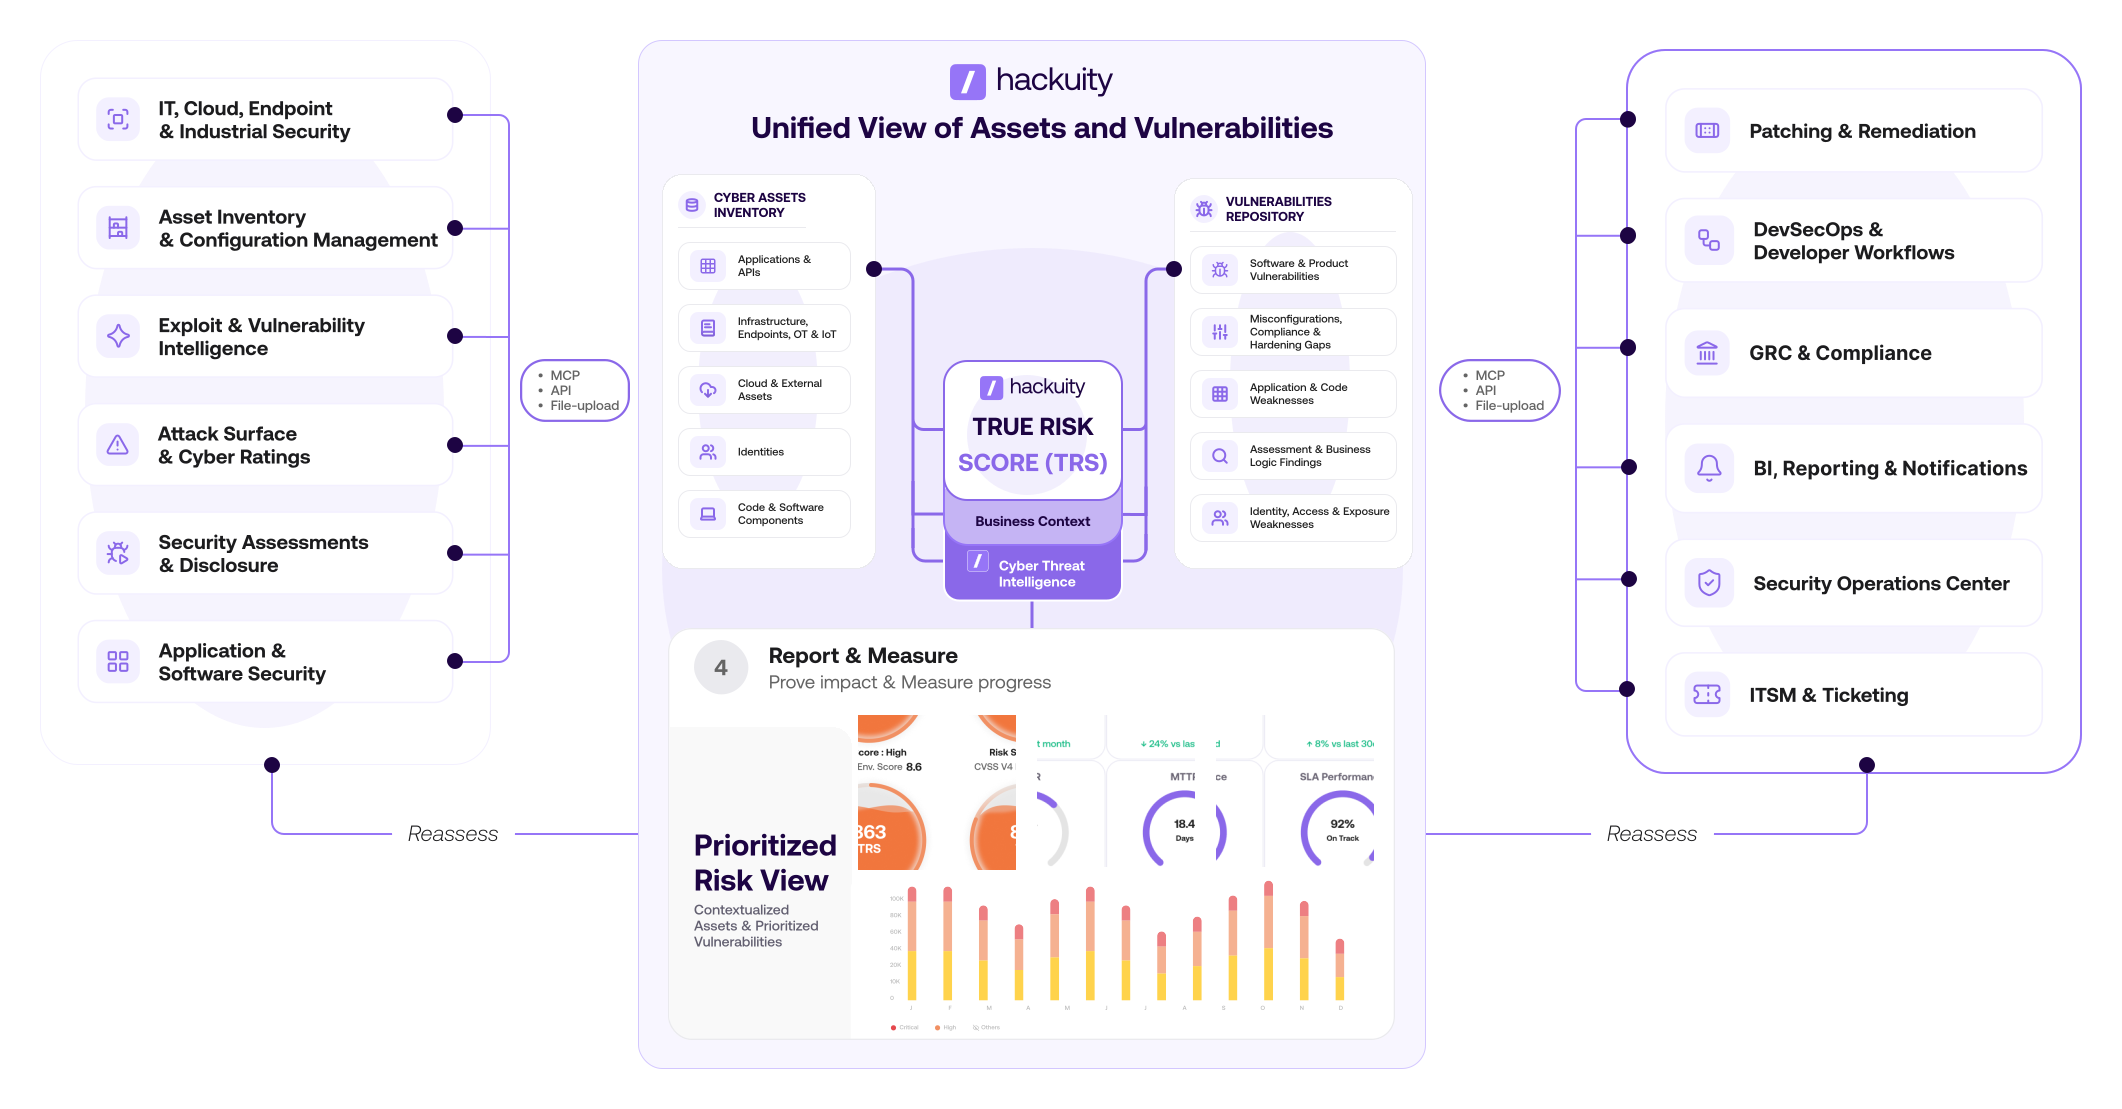
1 platform. 4 stages.

Every security tool generates findings and assets. Hackuity turns them into priorities, actions, and proof.
01
AGGREGATE & DEDUPLICATE

Bring every finding
into one place

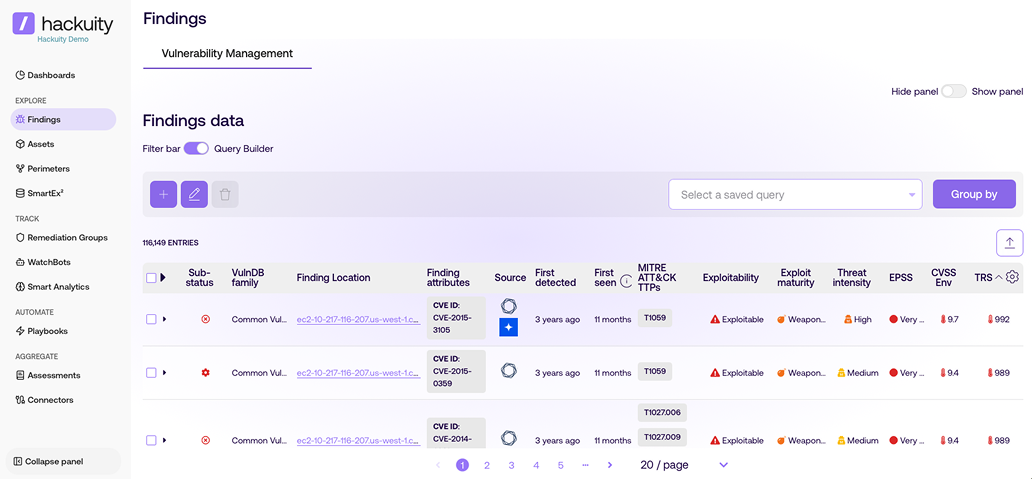
Security findings are scattered across scanners, cloud platforms, AppSec tools, CMDBs, and ticketing systems. Hackuity brings them together into a single, continuously updated view of your vulnerabilities, assets, and business context.
130+ connectors across scanners, cloud, AppSec, CMDB, endpoints, ITSM, and threat intelligence.
Automatic deduplication across all sources.
Asset context enrichment: business criticality, network exposure, ownership
Unified asset inventory, continuously updated
Coverage gaps identified across tools and environments
Explore Discover
Coming soon
Screenshot of the Hackuity Findings table listing 322 P0 findings with columns for CVE ID, location, source, TRS, EPSS, threat intensity, and exploit maturity
02
ENRICH & PRIORITIZE

Know what to fix first

Not every critical vulnerability is equally urgent. Hackuity uses True Risk Score (TRS) to identify the vulnerabilities that represent the highest risk to your organization. Every priority is backed by clear context, so your team can act with confidence.
True Risk Score: severity × threat × asset criticality
Enrichment with CISA KEV, EPSS v4, ransomware campaigns, and dark web signals
SmartEx² Enterprise: Recorded Future, Mandiant, CERT-IST…
Misconfigurations scored alongside CVEs: Active Directory, cloud environments
WatchBots: automatic CVE detection on your watched technologies
Explainable scoring: click to see exactly why a finding was prioritized
Explore Assess
Coming soon
Screenshot of the Hackuity Exposure Overview dashboard showing the full navigation sidebar and 325 critical, 5.2k high, and 110.7k other open findings, with a 12-month bar chart of findings by severity
03
AUTOMATE & ORCHESTRATE

Get vulnerabilities fixed faster

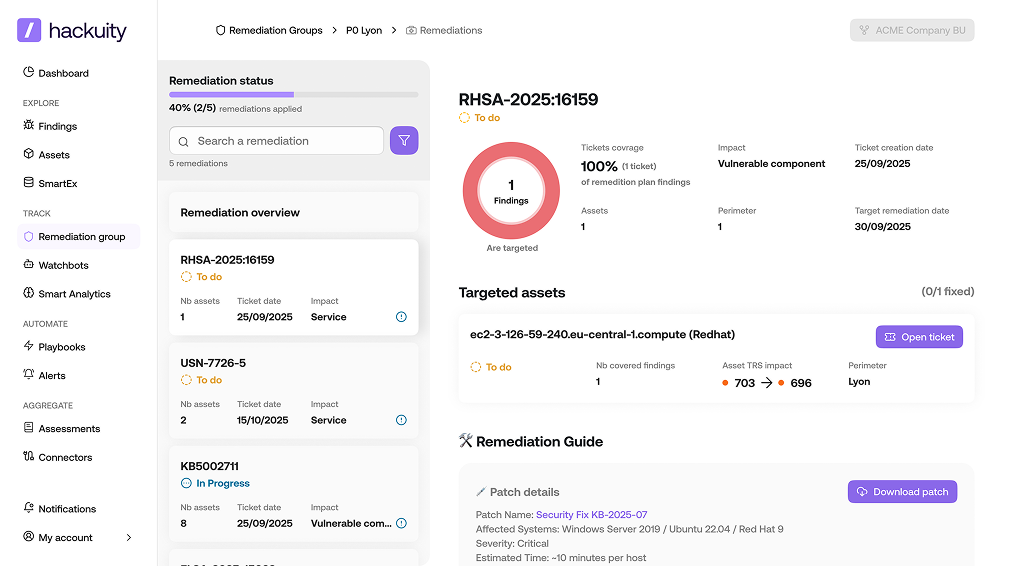
Hackuity routes findings to the right teams, generates AI-assisted patch guidance, and syncs bidirectionally with your ITSM tools without replacing your existing workflows. Humans stay in control while AI removes the friction.
Remediation Groups: bundle findings by patch : one action, maximum impact
Remediation Advisor: AI-assisted patch guidance, sequencing, and impact flags
Playbooks to automate routing, ticketing, and escalation
Bidirectional ITSM sync: ServiceNow, Jira, Azure DevOps, and more
Ownership tracking across security, IT, cloud, and application teams
Explore Remediate
Coming soon
Screenshot of the Hackuity Remediation Group interface showing the RHSA-2025:16159 remediation detail, 40% remediation progress, and a targeted asset with patch guidance
04
REPORT & MEASURE

Prove risk is going down

Every stakeholder gets the right view. The CISO gets a board-ready risk summary. The VM manager gets operational clarity. Regulators get audit-ready documentation automatically, from live data.
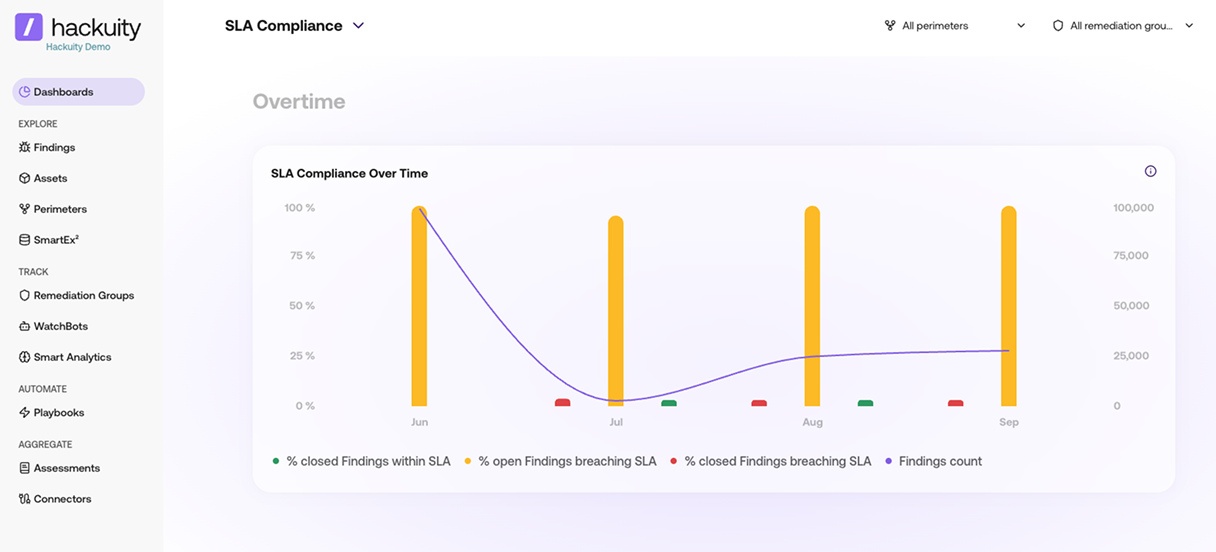
Executive view: risk trend, MTTR, SLA compliance
VOC Manager view: remediation velocity, backlog aging, automation rate
Compliance mapping: NIS2, VMMM, CRA, BOD 26-04
 Custom KPI builder to track what matters to your organization
Audit-ready evidence of decisions, ownership, and remediation progress
Explore Report
Coming soon
Screenshot of the Hackuity SLA Compliance dashboard showing a bar and line chart of SLA compliance and findings count from June to September
Vulnerability Operations isn't a one-time project. It's a continuous cycle of aggregation, prioritization, remediation, and measurement.
What is a VOC?
Coming soon
AI- ASSISTED OPERATIONS

AI where it helps. Human control where it matters.

Use AI to prioritize faster, validate findings, automate repetitive work, and generate reports
while keeping every decision transparent and under your control.
Remediation Advisor
AI-Powered patch prioritization
Beta sept/oct, GA Q4/Jan27
Coming soon
Ranks patches by aggregate risk score (TRS / SSVC), summarizes patching impact, and auto-creates ITSM tickets routed to the right team.
What should the cloud team fix first this week?
Probe Agent
AI-powered exploit validation
Beta Sept/oct, GA Q4/Jan27
Coming soon
Validate whether a vulnerability is actually exploitable in your environment and automatically update its priority, so teams focus on real threats instead of theoretical risk.
Is CVE-2026-4747 actually exploitable on our infrastructure?
VOC Copilot
Coming soon

Running a VOC means constant monitoring, reporting, and governance decisions.

Generates morning briefs, board-ready compliance reports (NIS2, BOD 26-04), configures SLA policies in natural language, and answers any VOC question 24/7.

What changed since the last executive review?
Scout Agent
AI-Powered Pentest Ingestion
MCP Beta ready, GA coming soon
Coming soon

Security assessments generate reports that take days to process manually.

Reads pentest and red team reports, maps findings and assets to your inventory. From PDF report to tracked finding: seconds, not days.

Ingest last week's red team report into the pipeline.

Works with the tools you already use.

Hackuity connects to your existing security and IT ecosystem, so you can unify vulnerability data, prioritize risk, and orchestrate remediation without replacing the tools your teams already use.
See all integrations
PROOF

The measured impact of Hackuity

0%
less manual work
Automate prioritization, remediation workflows, reporting, and ticket creation.
0%
Reduction in critical findings
Focus on the vulnerabilities that actually require immediate action.
0h+
of engineering work saved
Free security and engineering teams to focus on higher-value work.
$0M+
operational savings
Vulnerability Operations costs can exceed $M+. Reduce operational overhead.

Recognized by leading authorities.
CyberSecAsia Awards 2026
Seal of Excellence
Wavestone
Forrester
IMDA Accreditation
CyberSecAsia Awards 2025
SOC 2 Type 2
EcoVadis Committed
CyberSecAsia Awards 2026
Seal of Excellence
Wavestone
Forrester
IMDA Accreditation
CyberSecAsia Awards 2025
SOC 2 Type 2
EcoVadis Committed
CyberSecAsia Awards 2026
Seal of Excellence
Wavestone
Forrester
IMDA Accreditation
CyberSecAsia Awards 2025
SOC 2 Type 2
EcoVadis Committed

Still evaluating? Here’s what teams ask us most.

"We already have Qualys, Tenable, or Rapid7."

Hackuity does not replace your scanners. It makes them work better together. Your scanners detect. Hackuity consolidates, deduplicates, contextualizes, and prioritizes their findings in one place. Complementary, not competitive.

"Is this another dashboard to manage?"

No. Hackuity is an orchestration and prioritization layer. It automates repetitive vulnerability-management tasks and connects your findings to remediation workflows.

"Can we trust a European vendor?"

Yes. Hackuity is a European cybersecurity company, founded in 2020, SOC 2 Type II certified, and trusted by Fortune 500 enterprises.

"Is TRS really better than CVSS?"

TRS does not replace CVSS. It builds on CVSS and adds threat intelligence, asset criticality, exposure, and security controls to prioritize the risks that matter most in your environment.

"What about implementation effort?"

You can keep your existing tools and connect them incrementally. Hackuity is available as SaaS or on-premises, with standard connectors and onboarding support.

"Our team is small. We do not have the bandwidth."

That is precisely the use case. Hackuity automates consolidation, deduplication, and prioritization, reducing the manual reconciliation work required from your team.