













Vulnerability management has changed. Hackuity is built for what's next.
Vulnerability Management wasn't built for today's volume of findings, fragmented tools, or AI-driven threats. Hackuity helps security teams prioritize what matters, coordinate remediation, and reduce cyber risk.
Traditional Vulnerability Management has reached its limits.
With the rise of AI, the explosion in the number of vulnerabilities being discovered, and the shrinking time to exploitation, the environment changed and security teams don't need more visibility. They need a way to operate at today's scale.
Yesterday
Legacy Limits
Periodic infrastructure snapshots that worked when assets were static and teams were centralized.
10K+
Avg
Thousands of findings
Static vulnerabilities from siloed scans
Siloed security scanners and basic dashboards
Periodic network scanning schedules
Manual CVSS-based prioritization in Excel
VS
Today
Continuous Operations
Millions of dynamic cloud and application-layer assets exposed continuously to automated threats.
1M+
Critical
Millions of continuous findings
Continuous vulnerability exposure
Complex, interconnected cybersecurity stacks
Continuous real-time asset discovery & exposure
Explainable, AI-powered True Risk prioritization
The vulnerability tsunami isn't slowing down
AI is accelerating software development while helping attackers uncover new attack vectors and move faster than ever.
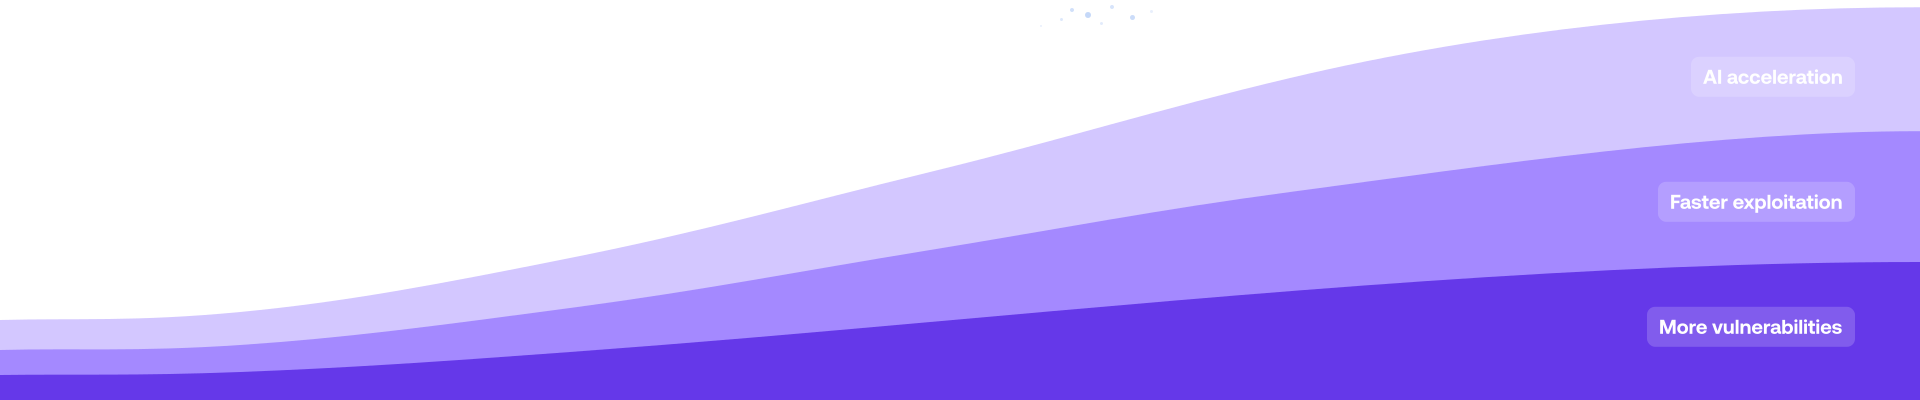
Finding vulnerabilities isn't the problem anymore.
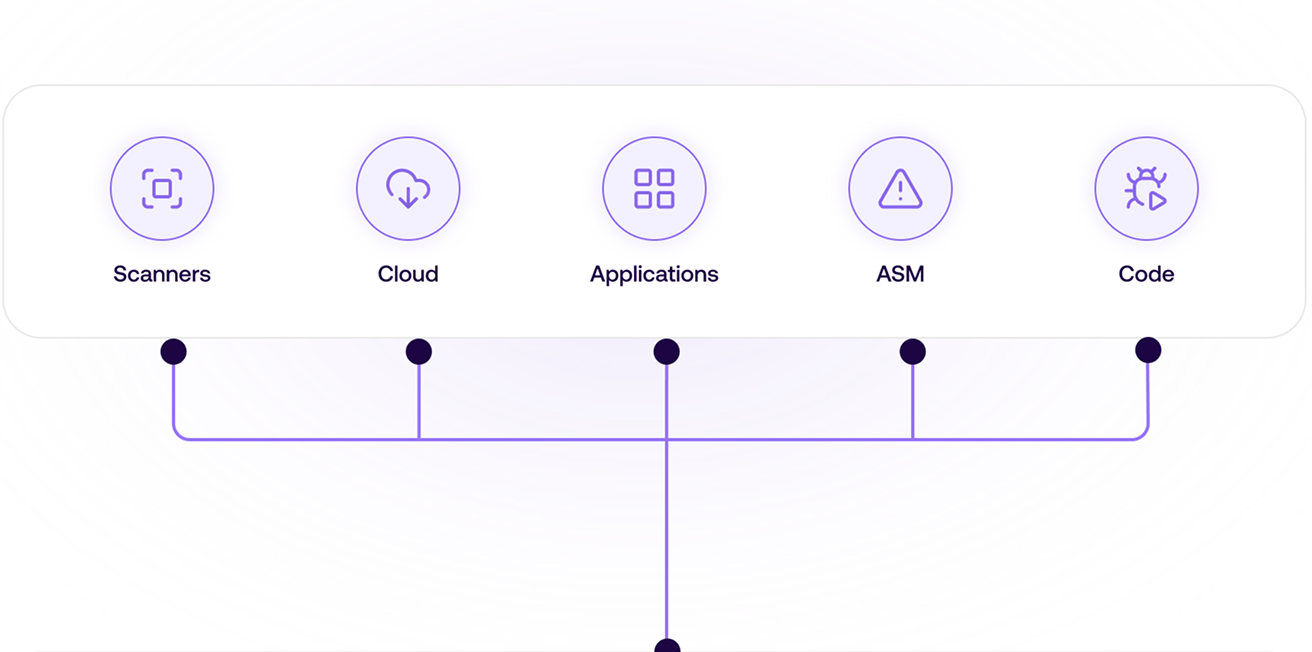
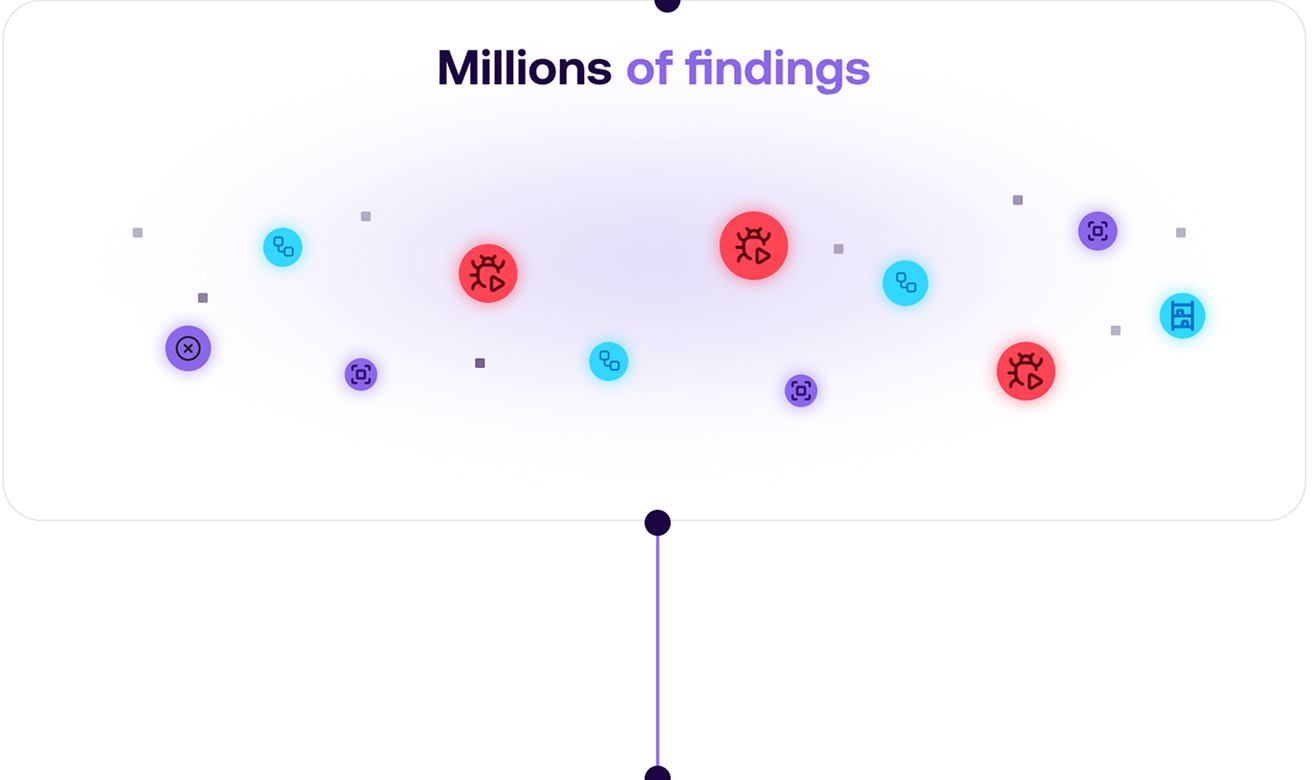
Vulnerability Operations is changing the game. Hackuity helps you lead it.
From AI-powered prioritization to coordinated remediation, Hackuity gives security teams the capabilities to operate at today's speed and scale.
01
Built for modern Vulnerability Operations
Run the full lifecycle from aggregation to absolute proof. Free your processes from vendor lock-in and avoid scanner feature taxes with a genuinely neutral system.
Aggregate
Prioritize
Automate
Report
02
Prioritize what actually matters
Hackuity's fully explainable True Risk Score (TRS) helps security teams focus on the 0.1% of CVEs that require immediate action, reducing critical findings by up to 99.9%.
TRS Explainability Factors
CVSS Severity + CISA KEV Exploits + Asset Criticality + Active Threats
03
Work with the tools you already trust
We connect with your existing scanners, cloud platforms, AppSec tools, LLM-powered detection sources, and ticketing workflows. We aggregate, normalize, and deduplicate findings without disrupting your existing security stack.

04
Deploy on your terms
Deploy in the environment that fits your organization. Choose between SaaS and On-premises without compromising functionality.
SaaS
On-Prem
05
Built to scale with your organization
Scale confidently across multiple business units, client environments, or diverse IT/OT/Cloud frameworks. Designed with absolute tenant isolation.
06
Proven by customers. Recognized by analysts.
Named in Forrester UVM Landscape Q1 2025 and Forrester Proactive Security Q1 2026. Certified with SOC 2 Type II compliance.
SOC 2 TYPE II
FORRESTER 2026
Hackuity vs. the alternatives
Not a takedown. A clearer way to understand where Hackuity fits.
CAPABILITY | SCANNER | GRC / RISK PLATFORM | HACKUITY |
|---|---|---|---|
Managed assets | Siloed to single vendor | Manual/API integrations | Designed for this (130+ connectors) |
Risk Prioritization | Generic CVSS metrics | Strategic qualitative scores | Explainable True Risk Score |
Remediation Orchestration | Simple notification emails | Ad-hoc task checklists | Automated SLA tracking & closure |
Deployment Flexibility | SaaS platform only | Typically standard SaaS | SaaS, On-Premise |
Explainability | Proprietary / Locked blackbox | Scoring based on configurable criteria | Fully traceable and explainable risk scores |
Best Fit | Single-tool focused teams | Compliance & compliance audits | Active Vulnerability Operations |
Asset Management | Limited to scanned assets | Separate CMDB often required | Unified cyber asset inventory |
COMPARE HACKUITY
Already using another platform?
See how Hackuity compares with the solutions security teams evaluate most often.
Hackuity vs Tenable
Understand where Tenable's scanning ends and Hackuity's full remediation orchestration operations layer begins.
Hackuity vs Brinqa
Evaluate modern operating workflow automation and connector flexibility against legacy vulnerability architectures.
Hackuity vs Nucleus Security
Compare multi-tenant operations, dedicated SaaS deployment capabilities, and complex SLA tracking structures.
BEFORE AFTER HACKUITY
What changes after Hackuity
BEFORE HACKUITY
Export findings from multiple tools, deduplicate manually
CVSS treats everything as High or Critical, nothing is truly prioritized
Create and route ITSM tickets one by one, without context
Build status reports manually every week and every quarter
AFTER HACKUITY
Unified finding queue, already prioritized by True Risk Score
TRS surfaces the 0.1% that requires immediate action
Tickets auto-generated, contextualized, and routed to the right team
Dashboards and compliance reports generated on demand
Proven business outcomes
0%
less manual work
Automate prioritization, remediation workflows, reporting, and ticket creation.
0%
Reduction in critical findings
Focus on the vulnerabilities that actually require immediate action.
0h+
of engineering work saved
Free security and engineering teams to focus on higher-value work.
$0M+
annual operational savings over the Exposure Program lifespan
Annual Vulnerability Operations costs can exceed $1M. Reduce operational overhead.



