






STEP 3 - AUTOMATE & ORCHESTRATE
Turn security priorities into action
Hackuity turns prioritized findings into governed remediation workflows, automatically routing work to the right owners, tools, and teams, and tracking every vulnerability through verified closure.
THE EXECUTION GAP
The gap between knowing and fixing
A risk score tells you what matters. Remediation requires ownership, coordination, execution, and proof. Without an orchestrated workflow, critical findings still get lost between security and IT.

Ownership gets lost
Findings are passed from one team to another without clear responsibility, accountability, or SLA.

Work gets stuck
Manual handoffs, scattered spreadsheets, and disconnected tools drag down remediation times while risks remain exposed.
Progress is hard to prove
Teams can't reliably show what was fixed, when it was fixed, or whether the active fix actually held.
THE OPERATIONAL LOOP
From prioritized finding to verified remediation
Hackuity connects prioritization, ownership, remediation workflows, and verification in one continuous operational loop.
01
Prioritized Finding
Real risk isolated
02
Identify Owner
Auto-routed to owner
03
Trigger Workflow
Jira/ServiceNow sync

Verified Closure
Scanner recheck confirms
01
PLAYBOOKS
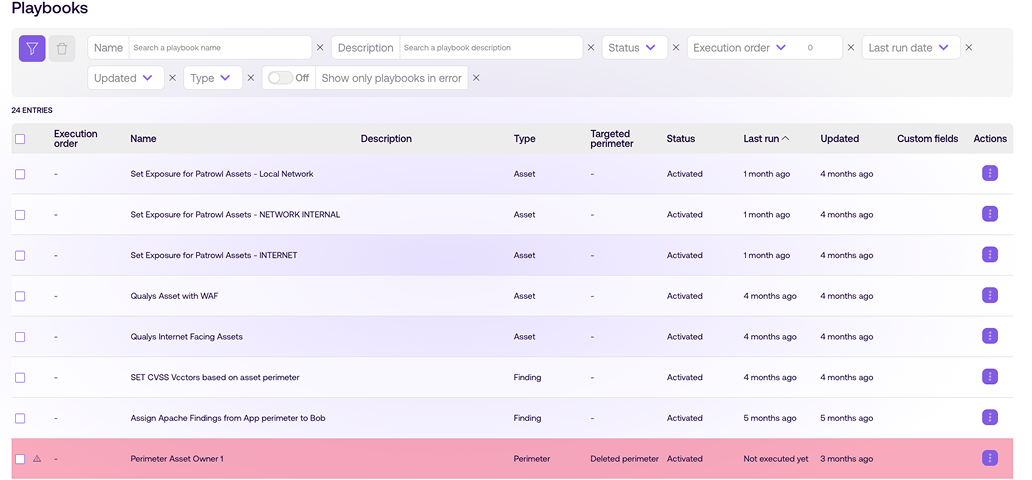
Automate the next step
Use reusable Playbooks to trigger remediation actions based on vulnerability context, priority, asset criticality, or ownership. Turn complex playbook logic into automated guardrails.
IN DEVELOPMENT - 2026
The Remediation Advisor will recommend the next best action when no Playbook rule covers the case.
02
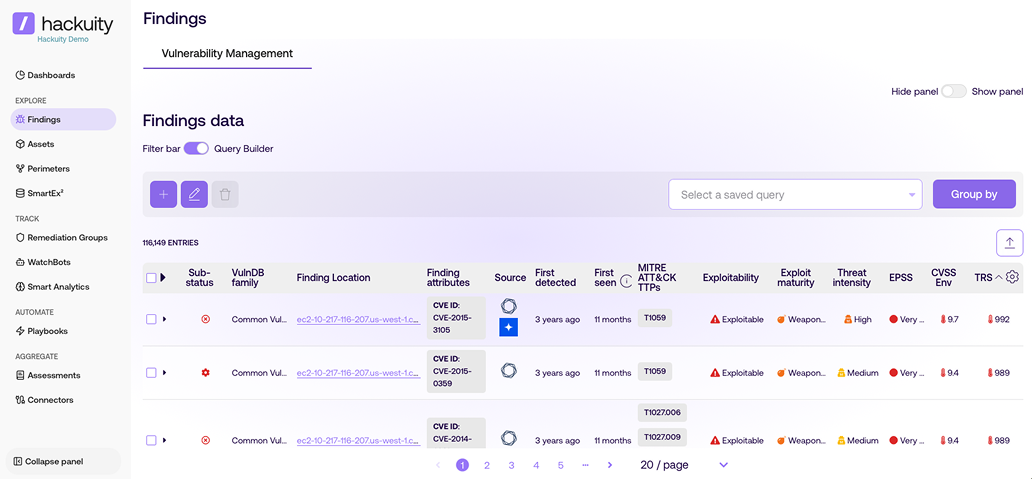
ROUTING & OWNERSHIP
Send work to the right owner
Automatically route remediation based on asset ownership, business context, application teams, or organizational rules. No manual triage or finger-pointing.
03
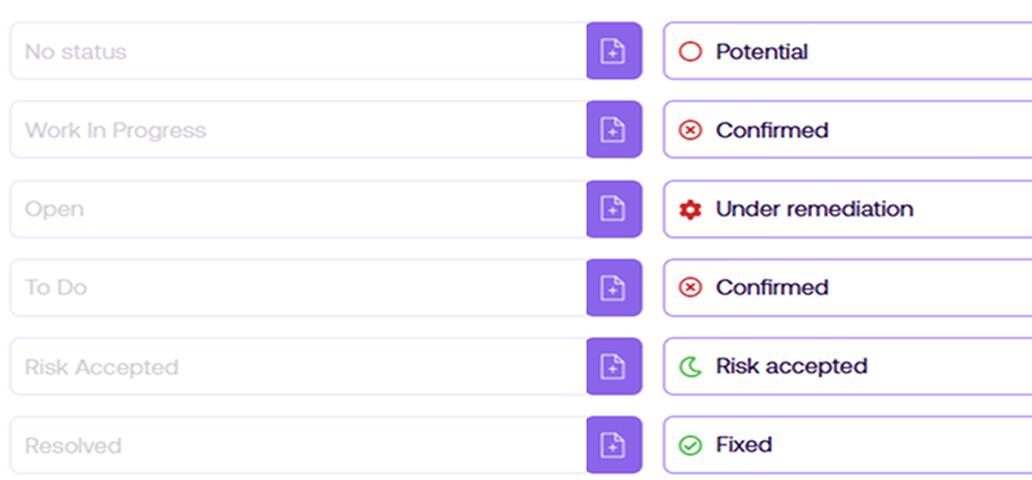
VERIFICATION
Close with confidence
Hackuity tracks remediation through the full lifecycle and verifies closure using updated security scanner data, not just ticket state.
What changes in the day-to-day?
Without Orchestration
Raw, unprioritized findings passed blindly between teams
Manual ticket creation and endless chasing of owners
Unclear asset ownership delaying critical actions
Tickets closed manually without scanner-proven proof of fix
VS
With Hackuity
Prioritized work routed with rich, actionable technical context
Automated routing through rule-based Playbooks
Clear ownership mapping from the start of the lifecycle
Automatic closure verified dynamically by scanners
130+ INTEGRATIONS
Works with the tools your teams already use
Hackuity connects vulnerability operations with the systems your remediation teams already rely on.
Explore 130+ integrations

MEASURE IMPACT
Fix what matters. Measure the impact.
Remediation doesn't end when a ticket is closed. Hackuity keeps a complete record from prioritization to verified remediation, giving security teams the evidence and metrics needed to measure operational performance and risk reduction.
~0 Days
Mean Time To Remediate (MTTR)

MTTR
Tracked monthly, by severity and remediation group
~0%
SLA Performance
Within defined guardrails
SLA Performance
Within defined guardrails
0+
Verified Closures
100% scanner confirmed
Verified Closures
Every closure scanner-confirmed, not just ticket-confirmed"
WHAT COMES NEXT
Fix what matters. Measure the impact.
"Remediation is not complete when a ticket is created or manually closed. Hackuity gives security teams a reliable record of what was prioritized, who acted, what changed, and when the fix was confirmed. That is what Step 4 delivers.
THE REPORTING GAP

MTTR is tracked nowhere. You cannot improve what you cannot measure.
Boards ask for risk trend data. Security teams produce ticket counts. Not the same thing.
Auditors need proof of what happened, not raw tickets. Manual exports and spreadsheets
do not cut it at enterprise scale.
do not cut it at enterprise scale.
Discover how Hackuity measures risk reduction
4
Report & Measure
STEP 4 REPORT & MEASURE
Hackuity gives security teams a reliable record of what was prioritized, who acted, what changed, and when the fix was confirmed. It includes prioritized findings, assigned owners, campaign and ticket status, SLA performance, scanner-confirmed remediation, complete remediation history, and audit-ready evidence.
COMMON QUESTIONS
Orchestration in practice
Does Hackuity replace our ITSM?


No. Hackuity orchestrates the security routing workflow while Jira, ServiceNow, or Ivanti remains the operational system of record for IT teams.
Automate & Orchestrate
How does Hackuity automate remediation?
Hackuity Playbooks apply configurable rules to incoming findings and assets, instantly triggering appropriate ticketing, SLA assignment, and notifications automatically
Automate & Orchestrate
How does Hackuity determine vulnerability ownership?
It extracts metadata from asset repositories, CMDB synchronizations, application tags, and organizational rules to map the appropriate team from day one.
Automate & Orchestrate