













Article
Blog
Insights, research, and practical guidance to help security teams prioritize risk, accelerate remediation, and stay ahead of modern threats.
Most recent
Hackuity in the News
5 minutes
read
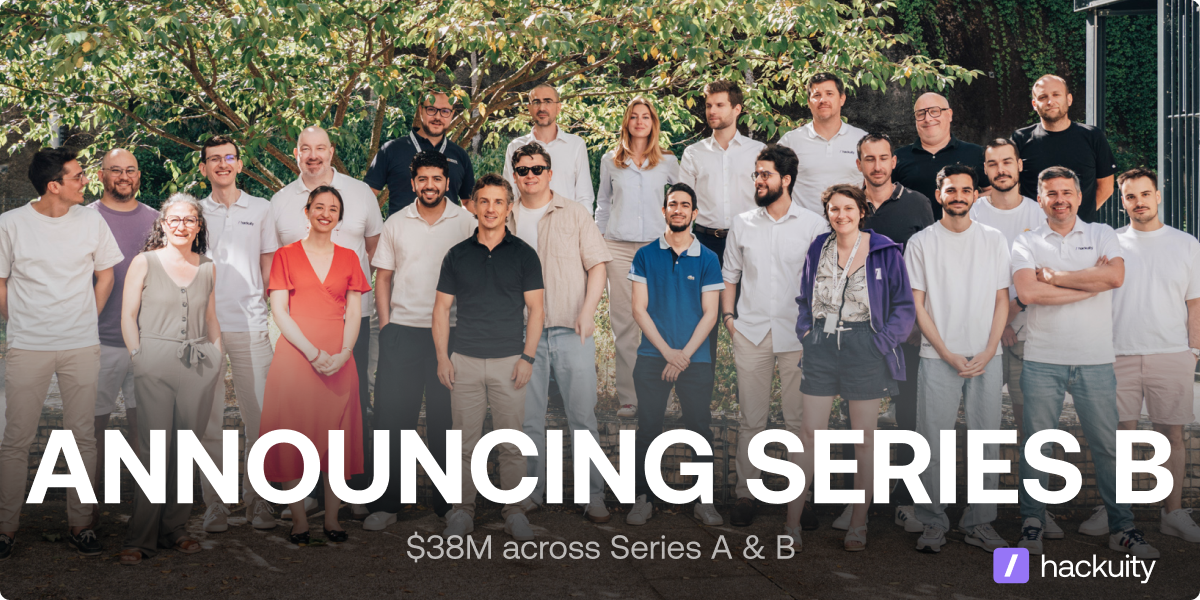
Hackuity raises $19M Series B to scale the AI-powered Vulnerability Operations Center
Today we announced $19 million in new funding, bringing Hackuity's total funding to $38 million. The round was led by Forgepoint Capital International, alongside our existing investors Bright Pixel, Bpifrance and Seventure Partners.
September 16, 2026
Library
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Article
Expert View
8 minutes
read
Copy Fail (CVE-2026-31431): Universal Linux privilege escalation requires immediate action
"An unprivileged local user can write 4 controlled bytes into the page cache of any readable file on a Linux system, and use that to gain root." - Source: Xint Security Research copy.fail A nine-year-old optimization in the Linux kernel turned into a universal privilege escalation path. Public PoCs dropped immediately, major cloud providers are scrambling to patch, and CISA added it to the Known Exploited Vulnerabilities catalog on May 1st. If you run Linux anywhere (and you do), this is a "patch first, analyze later" situation.
August 25, 2026
Hackuity in the News
5 minutes
read
More code and faster attacks mean a rethink for vulnerability management
The relationship between vulnerability disclosure and exploitation is fundamentally changing. Where security teams once had weeks to assess and respond to most newly reported CVEs, attackers are now moving in a matter of days. Research has found that the exploitation of high and critical vulnerabilities rose 105% year-on-year in 2025, with the median time from disclosure to active exploitation falling to just five days.
August 25, 2026
Article
Expert View
8 minutes
read
The NVD Just Changed the Rules. Here's What That Actually Means for Your Vulnerability Program
On April 15, 2026, NIST announced they can no longer keep up with the flood of CVE submissions hitting the National Vulnerability Database. The numbers tell the story: CVE submissions jumped 263% between 2020 and 2025, and even after enriching a record 42,000 CVEs last year, the backlog keeps growing. So they're changing how NVD works. And if your vulnerability management workflow depends on NVD enrichment, you need to understand what's shifting.
August 25, 2026
Expert View
5 minutes
read
When Comparison Becomes Marketing Theater: A Quick Reality Check on DefectDojo’s “Analysis” of Hackuity
Our friends at DefectDojo recently published a comparison piece positioning their platform against Hackuity. The article is here: DefectDojo Pro vs Hackuity in 2026: The Risk Cockpit vs. The Security OSFirst, credit where it’s due: writing comparison content is hard. It takes time, effort, and a willingness to step into uncomfortable territory. We genuinely appreciate it, if only because this kind of content tends to appear when something in the market is shifting. Rapid customer replacement, international expansion, and increased visibility tend to… trigger reactions. And that’s fine. Disruption usually does. Because that’s the real point: Hackuity isn’t just another “vulnerability management tool.” The goal has always been to move beyond fragmented, inefficient processes and into something operationally coherent, what we call VulnOps. Now, let’s address a few highlights from the article.
August 25, 2026
Expert View
Product
10 minutes
read
After Glasswing: Why AI-Driven Vulnerability Discovery Makes Exposure Management Platforms Essential
On April 7, 2026, Anthropic launched Project Glasswing. The announcement sent shockwaves through the cybersecurity industry, not because of what it promised, but because of what it revealed. Claude Mythos Preview, an AI model with 10 trillion parameters, had autonomously discovered thousands of zero-day vulnerabilities across every major operating system and web browser. Some had existed for 27 years. Others had survived 5 million automated scans. As one industry analysis put it: "The vulnerability pipeline just got a firehose attached to it."
August 25, 2026
Expert View
Product
10 minutes
read
Claude Mythos and Project Glasswing: How AI Is Reshaping the Cybersecurity Battlefield
You’ve obviously seen this announcement everywhere already, but Anthropic’s latest reveal is still worth a closer look. The company has introduced Claude Mythos Preview, a new AI model described as its most powerful to date, capable of autonomously discovering and exploiting software vulnerabilities at a level comparable to, or even exceeding, top human security researchers. The company deemed this model too dangerous for public release. Instead, they're deploying it through a controlled initiative that could reshape how we think about software security.
August 25, 2026



