





FOR CISOS
Stop reporting on findings.
Start reporting on risk.
You’re accountable for cyber risk, but most vulnerability programs give you fragmented data, technical scores, and millions of findings. Hackuity turns vulnerability data into a clear view of where you’re exposed, what matters, and whether risk is going down.
THE REALITY FOR SECURITY LEADERS
Accountable for risk. Without a clear picture of it.
SEVERITY NOISE
Findings everywhere, clarity nowhere
Scanners, AppSec, cloud, ASM, pentests, and other tools all produce their own version of risk.
TRANSLATION GAP
CVSS doesn't translate to boardrooms
Raw technical severity scores do not explain critical business impact, revenue exposure, or remediation urgency to your executives.
COMPLIANCE RISKS
Regulators want evidence, not dashboards
NIS2, DORA, and CISA directives mandate strict, documented SLAs, clear audit trails, and concrete risk outcomes.
COMPLIANCE RISKS
Teams work in separate silos
Security, IT Operations, DevOps, and GRC teams do not share a single, unified view of what to fix and when, leading to remediation gridlocks.
NO METRICS
You can't prove risk is going down
Without continuous, standardized metric baselines, every executive conversation or board report starts entirely from scratch.
DISCONNECTED ASSET INVENTORY
You don’t have a reliable view of your assets
Asset data is fragmented across tools, with no unified repository to consolidate, deduplicate, and enrich your assets.
WHAT YOU GAIN WITH HACKUITY
From exposure noise to measurable risk reduction
UNIFIED VISIBILITY
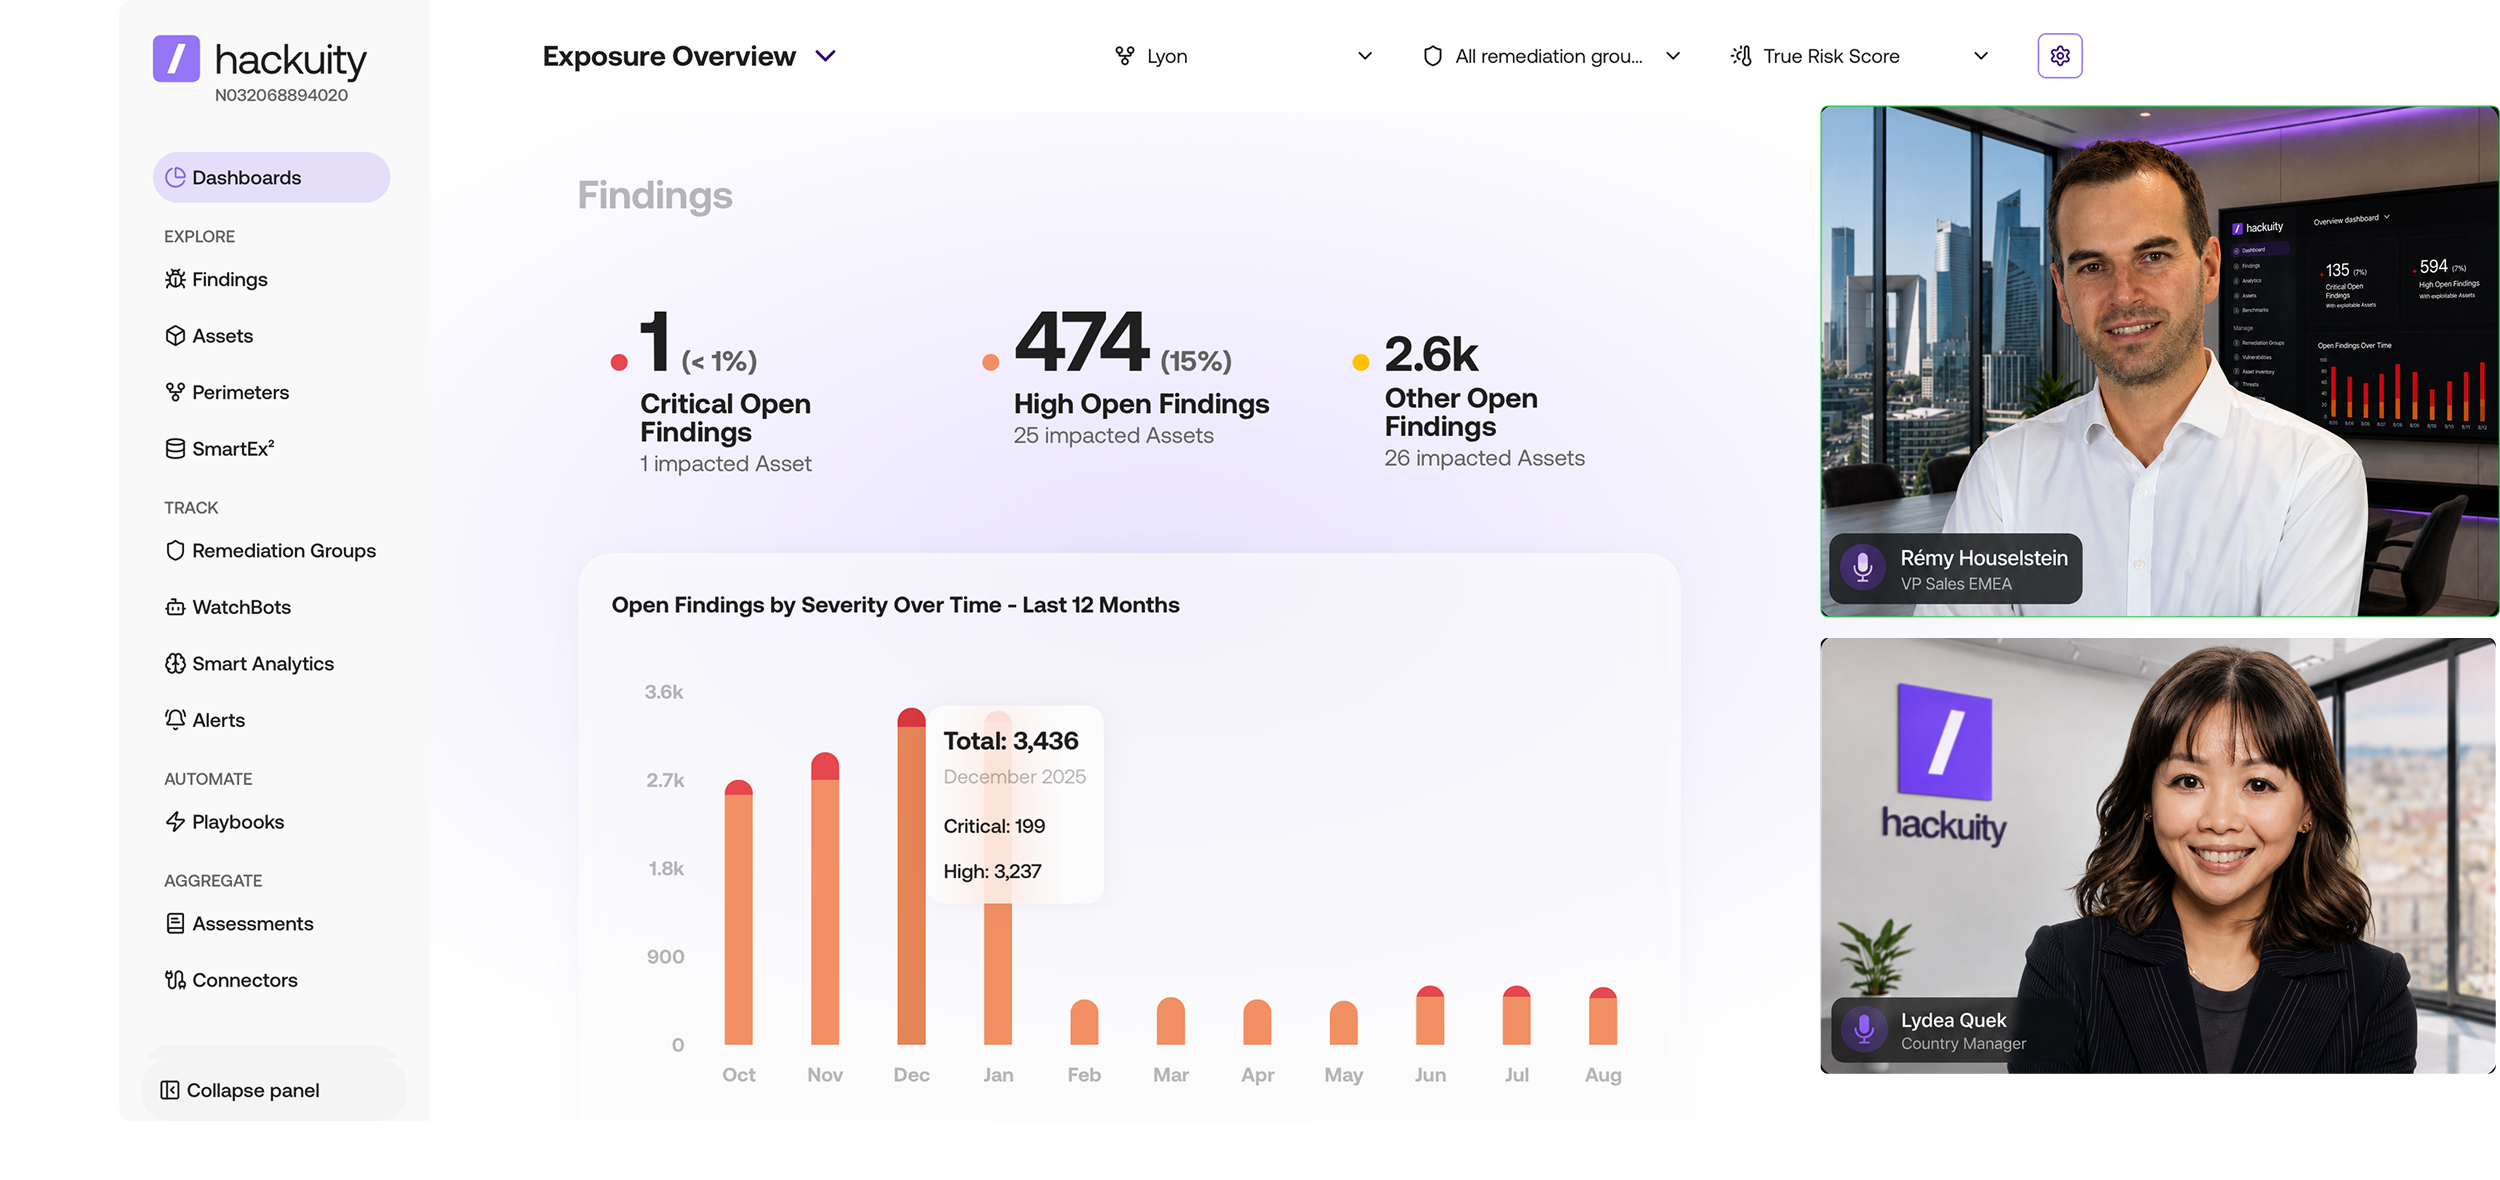
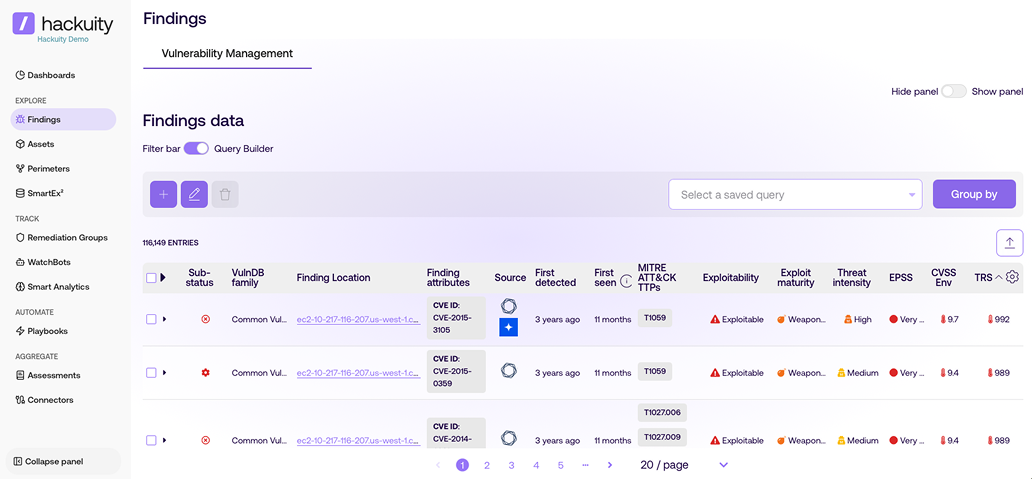
1 view of your entire attack surface
Hackuity unified attack surface view consolidating assets and vulnerability findings from 130+ security tools
From fragmented signals to a single exposure map.
RISK CLARITY
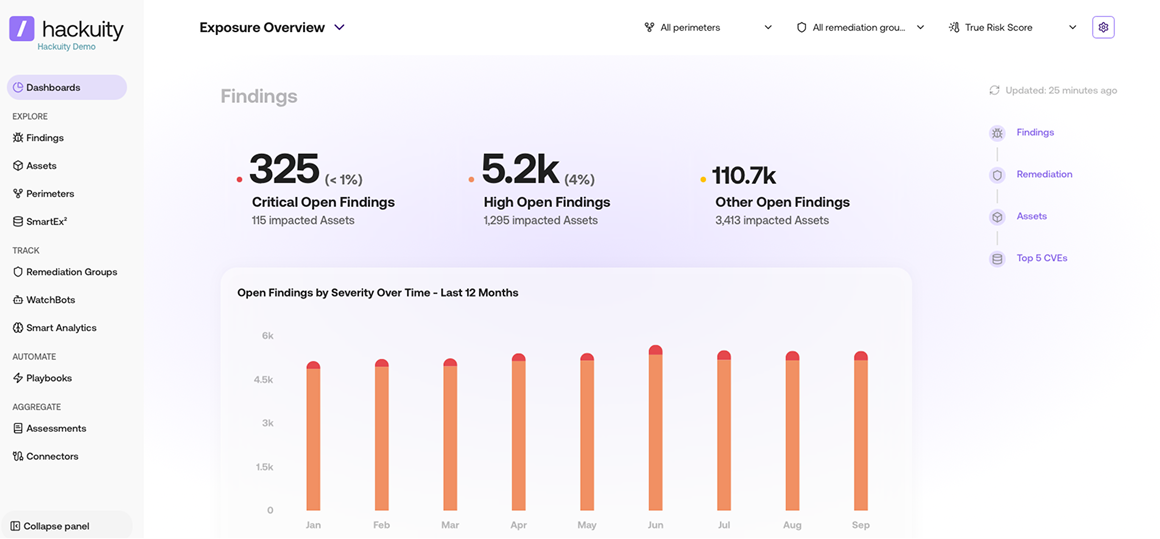
True Risk Score: know the 1% that actually matters
Hackuity's True Risk Score automatically combines CVSS with exploit intelligence, threat context, and asset criticality. The result: out of hundreds of thousands of CVEs, your team knows exactly which findings require immediate action, and which can wait.
0.01%
of findings require immediate remediation after TRS.
From millions of findings to a prioritized, defensible action list.
BOARD-READY REPORTING
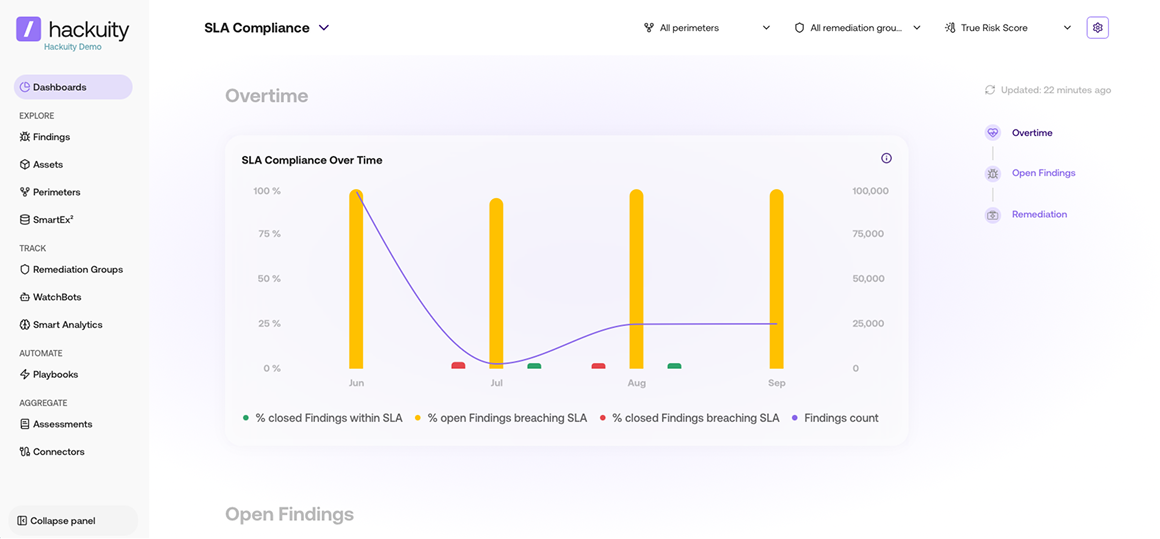
Explain risk in business terms, not technical scores
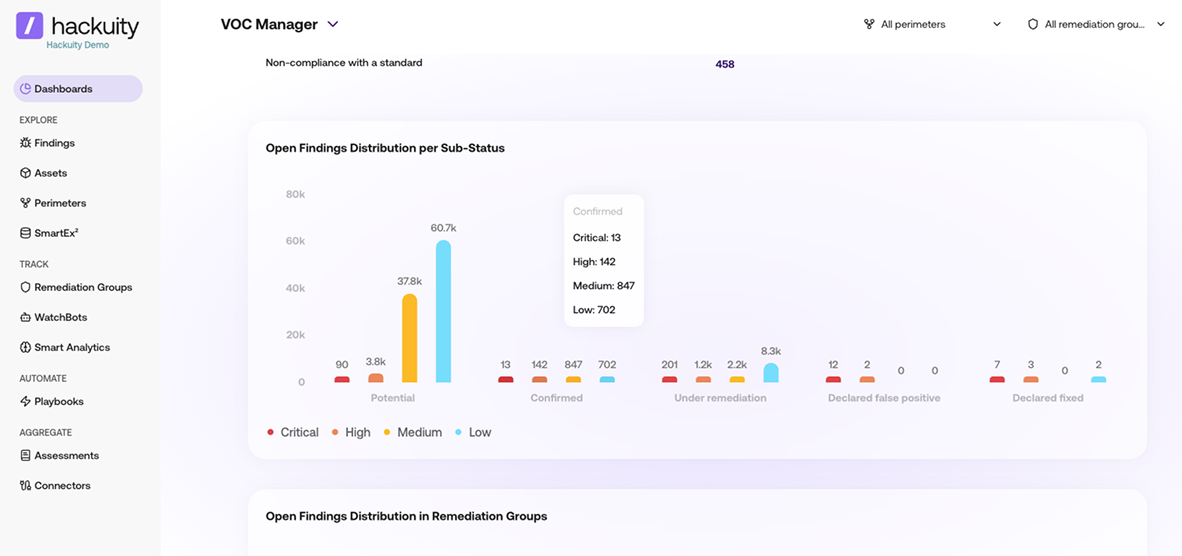
Risk posture dashboards, SLA compliance rates, MTTR trends, and exposure reduction over time - all available on demand through off-the-shelf dashboards or customizable dashboards with Smart Widgets. Generate compliance summaries for NIS2, DORA, or CISA BOD 26-04 without manual work.
From quarterly fire drills to real-time governance.
OPERATIONAL EFFICIENCY
Your team does more, without growing headcount
Hackuity automates vulnerability triage, SLA assignment, ITSM ticket routing, and remediation tracking. Security teams reclaim analyst time previously spent on manual qualification.
70%
of VM operations automated · $125K saved per year on 3-person team.
From quarterly fire drills to real-time governance.
THE NUMBERS THAT MATTER TO A CISO
Measure risk reduction, not finding volume
0%
Reduction in critical findings
Your team focuses on what truly requires action.
x0
Faster remediation
Reduce MTTR for vulnerabilities that matter most.
$0M+
annual operational savings
Run VOC at enterprise scale with less overhead.
COMPLIANCE
Turn regulatory requirements into operational action
Hackuity helps security teams translate regulatory requirements into clear vulnerability priorities and remediation actions.
NIS2
Risk-based prioritization, documented SLAs, and full audit trail per individual finding to meet critical infrastructure guidelines.
DORA
Continuous threat-exposure monitoring, incident-linked vulnerability tracking, and real-time posture dashboard reports.
CISA BOD 26-04
SLA deadlines auto-assigned per finding on ingestion, automated KEV-aligned exploit intelligence tracking.
PROOF
Trusted by leading enterprises
Before Hackuity, we were drowning in over 100,000 active alerts. Within three weeks, we contextualized our actual exposure and routed the critical 1% that mattered. It completely bridged the gap between our security and engineering teams.
Alex Mercer
CISO, Global Fintech Corporation

98%
Reduction in critical findings
3x
MTTR improved
94%
SLA compliance rate
80h
Manual reporting saved/mo
Recognized by leading authorities.
CyberSecAsia Awards 2026
Seal of Excellence
Wavestone
Forrester
IMDA Accreditation
CyberSecAsia Awards 2025
SOC 2 Type 2
EcoVadis Committed
CyberSecAsia Awards 2026
Seal of Excellence
Wavestone
Forrester
IMDA Accreditation
CyberSecAsia Awards 2025
SOC 2 Type 2
EcoVadis Committed
CyberSecAsia Awards 2026
Seal of Excellence
Wavestone
Forrester
IMDA Accreditation
CyberSecAsia Awards 2025
SOC 2 Type 2
EcoVadis Committed
See Hackuity in action
Schedule a personalized demo to see how Hackuity maps to your environment.