Traditional Vulnerability Management wasn’t built for the AI era

AI is creating vulnerabilities faster than humans can prioritize and remediate them. Organizations need a VOC that gives security teams the operational layer to keep up.
0B+
Findings
0M+
Assets managed
0+
Users connected
0+
integrations

The vulnerability landscape changed. Your workflows didn’t.

Post-Mythos is increasing vulnerability volume. AI is accelerating everything around it and security teams need a new way to operate at scale.

Without a VOC More findings, more noise

Security teams are already overwhelmed. Post-Mythos and AI only increase the pressure.
Findings scattered across security tools
CVSS-only prioritization
Duplicate and conflicting findings
Manual tracking and chasing owners

The bottleneck gap Finding is fast, fixing is slow

Detection keeps accelerating. The work between finding and remediation remains painfully manual.
Critical queues nobody can clear
Invisible SLA breaches
Unassigned ticket ghost-towns
Security-to-IT handoff delays

With Hackuity VOC AI-powered operations at vulnerability scale.

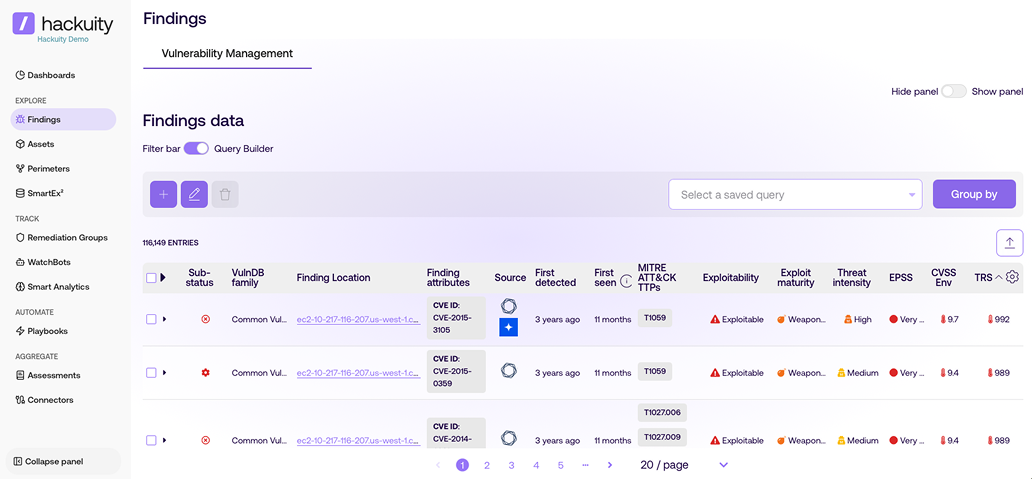
Unified, normalized & deduplicated findings
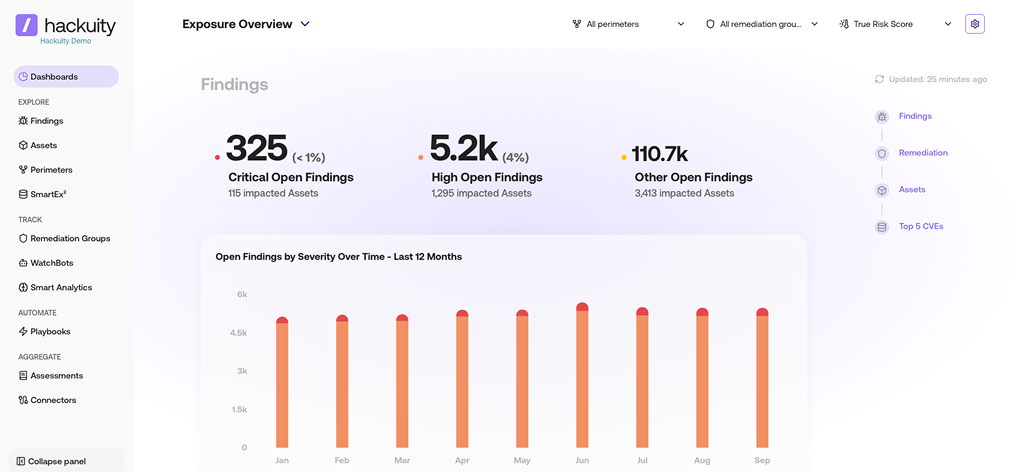
Threat-informed True Risk prioritization
AI-assisted triage & remediation
ITSM-orchestrated workflows
Verified closure & real-time audit trail

How a Vulnerability Operations Center works

A VOC connects everything between finding a vulnerability and getting it fixed. One operational layer across your scanners, assets, risk context, remediation teams, and workflows.
01

AGGREGATE & DEDUPLICATE

1 view of everything
Connect every scanner, cloud tool, AppSec source, ASM, pentest, and bug bounty. Hackuity normalizes, deduplicates, and enriches findings & assets into one vulnerability backlog.
130+ native connectors
Cross-scanner deduplication
No scanner bias
Pentest & bug bounty in the same inventory
Long-term vulnerability history & assets
130+
native connectors into one exposure map
02

ENRICH & PRIORITIZE

Stop triaging noise
Hackuity enriches every finding with threat intelligence, exploitability, EPSS, CISA KEV, asset criticality, and business context, then prioritizes what represents real risk.
99% fewer critical findings
Every priority explainable
Surfaces exploited vulns first
SmartEx² security intelligence
MITRE ATT&CK mapping
03

AUTOMATE & ORCHESTRATE

Priority to ticket to verified closure
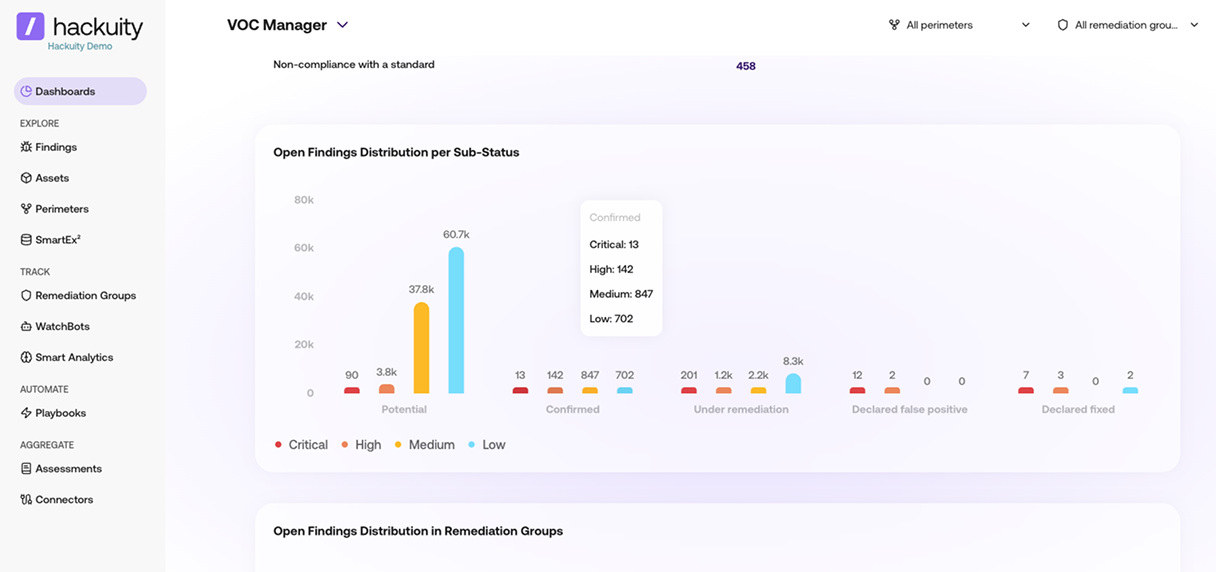
Route vulnerabilities to the right teams, create ITSM tickets, enforce SLAs, and track remediation through closure. AI helps teams understand what to fix and how.
Jira/ServiceNow/Azure DevOps sync
SLA policies by criticality
Intelligent Remediation groups
AI Remediation Advisor assistance
MCP Server natural language queries
04

REPORT & MEASURE

Show cyber risk is going down
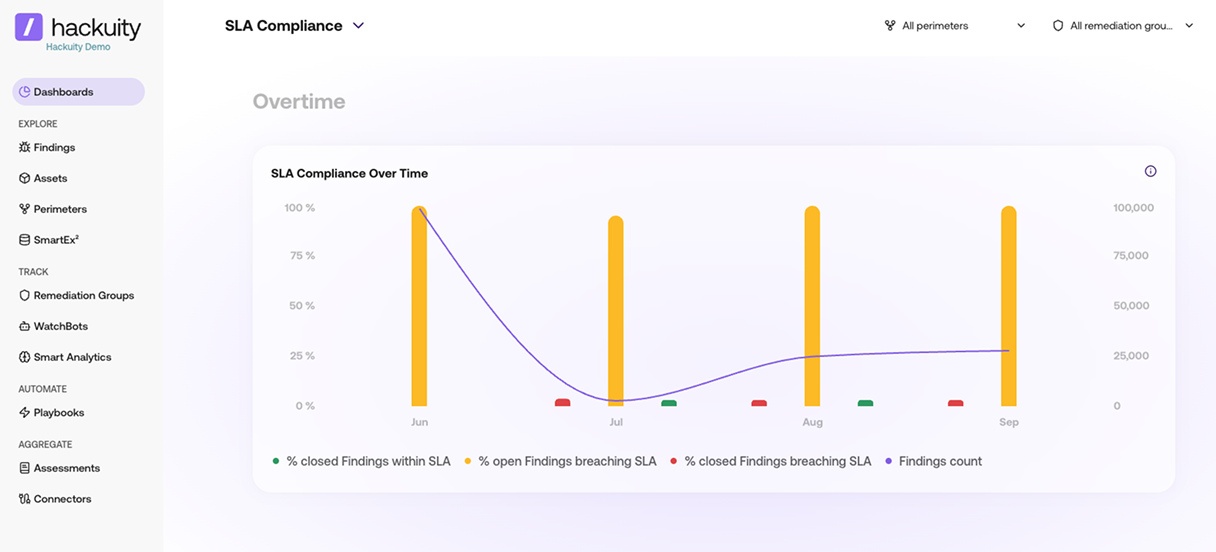
Turn remediation activity into proof of risk reduction. Track exposure, MTTR, SLA performance, vulnerability aging, and verified closure across your organization.
MTTR by risk & criticality
SLA compliance & breaches
Vulnerability aging & backlog trends
Risk reduction over time
Executive & audit-ready reporting
AI IN YOUR VOC

AI where it removes friction. Not where it creates a black box

Evidence Trail

SmartEx²

Real-time vulnerability intelligence. Exploit maturity, dark web monitoring, MITRE ATT&CK TTPs mapped directly to CVEs.
‍
"CVE-2024-XXXX : actively exploited in the wild for 3 days. 12 assets affected in your production perimeter."
Verifiable against source data
Why this recommendation

MCP server

Ask anything about your vulnerability data, in plain language. Get instant answers on assets, findings, ownership, SLAs, and exposure.
"Show me all critical findings in production assets owned by Team A with SLA breached"
Verifiable against source data
Human Validation

Remediation Advisor

AI-assisted remediation plans based on asset context, team structure, patch history, and deployment impact analysis.
Recommended: patch kernel version across 47 assets. Estimated effort: 2h. Closes 312 findings.
Verifiable against source data

Built for everyone running Vulnerability Operations

VM Manager / Head of VOC

Run the vulnerability lifecycle from one operating system.

CISO

See exposure, remediation performance, and risk reduction in one place.

MSSP / Security Service Provider

Run multiple client VOCs without multiplying operational overhead.

Deploy your VOC your way!

Whether you require fully-managed cloud services or self-hosted air-gapped environments, Hackuity supports your security topology.

Cloud SaaS

Full capabilities available instantly, faster time-to-value, managed automatically by Hackuity experts.

On-Premises

Run entirely inside your own air-gapped secure networks for absolute control of intelligence databases.

Questions teams ask before building a VOC

What is the difference between a SOC and a VOC?

A SOC detects and responds to active threats and incidents. A VOC manages vulnerability risk before it becomes an incident. It connects findings & assets, risk context, ownership, remediation, and reporting into one continuous operation.

VOC

Does a VOC replace our vulnerability scanners?

No. Your scanners keep doing what they do best: finding vulnerabilities. A VOC sits above them, unifying findings, removing duplicates, prioritizing real risk, and orchestrating remediation.

VOC

What if the same server is reported by five different tools?

A.C.E evaluates each source entry against a weighted Decision Tree. Once a match is found (e.g. FQDN), the engine stops and creates a single unified asset enriched with data from all five sources. No double-counting.

VOC

Why do we need a VOC if we already have a Vulnerability Management platform?

Deployment time depends on the number of integrations, assets and client environments. Teams can typically start with an initial operational scope within a few weeks.

VOC

How does AI fit into a VOC?

AI helps teams operate vulnerability data at a scale humans can't manage manually. Hackuity uses AI to enrich context, accelerate investigation, prioritize risk, and recommend remediation.

Humans keep control of the decisions.

VOC

Can Hackuity work with our existing security stack?

Yes. Hackuity is vendor-neutral and connects with 130+ security tools and platforms, including scanners, AppSec tools, cloud platforms and ITSM systems.

VOC

How long does it take to build a VOC?

You don't need to build everything from scratch. Hackuity connects to your existing security and IT tools, centralizes findings, and adds prioritization and remediation workflows on top.

VOC

Ready to modernize your Vulnerability Operations?

We will run a fit assessment based on your actual stack, asset volume, and current vulnerability load - in 30 minutes.

VOC Launch Sequence

1
Connect your stack
Zero-friction scanner integrations
2
Prioritize what matters
Generate contextual True Risk Scores
3
Route remediation
Push orchestrated tickets to the right teams
4
Prove progress
Validate closed vulnerabilities automatically