Your team spends too much time on work that shouldn't require human effort.

Security teams don't struggle because they lack expertise. They struggle because their workflows don't scale, triage is manual, tickets are created one by one, follow-ups happen over email. Hackuity automates the repetitive work, so analysts can focus on high-value tasks instead of data crunching.

Where your team's time actually goes

The majority of VM analyst time is spent on repetitive coordination work instead of security analysis.
01

Juggling outdated or incomplete asset inventories.

02

Manually scoring and qualifying each finding

03

Creating and routing ITSM tickets without enough context to prioritize them.

04

Chasing IT teams for remediation updates

05

Painfully building weekly and monthly status reports manually in Excel.

THE EFFICIENCY GAP

Manual vulnerability management doesn't scale.

Even skilled teams lose time when every tool speaks a different language and every remediation step requires manual coordination.
01
Detect
02
Export
03
Deduplicate
04
Score
05
Ticket
06
Chase
07
Report
Before: manual workflow
Every arrow is a person
End of day: still behind, backlog growing
4+ scanners, 4 different formats
−/−
CSV exports, every scan cycle
−/−
Same CVE, three tools, three scores
−/−
CVSS scored by hand, one by one
−/−
Tickets typed manually, no context
−/−
Follow-ups by email and meetings
−/−
Hours rebuilding Excel reports
With Hackuity: one continuous pipeline
Every arrow is automated
End of day: backlog structured and shrinking
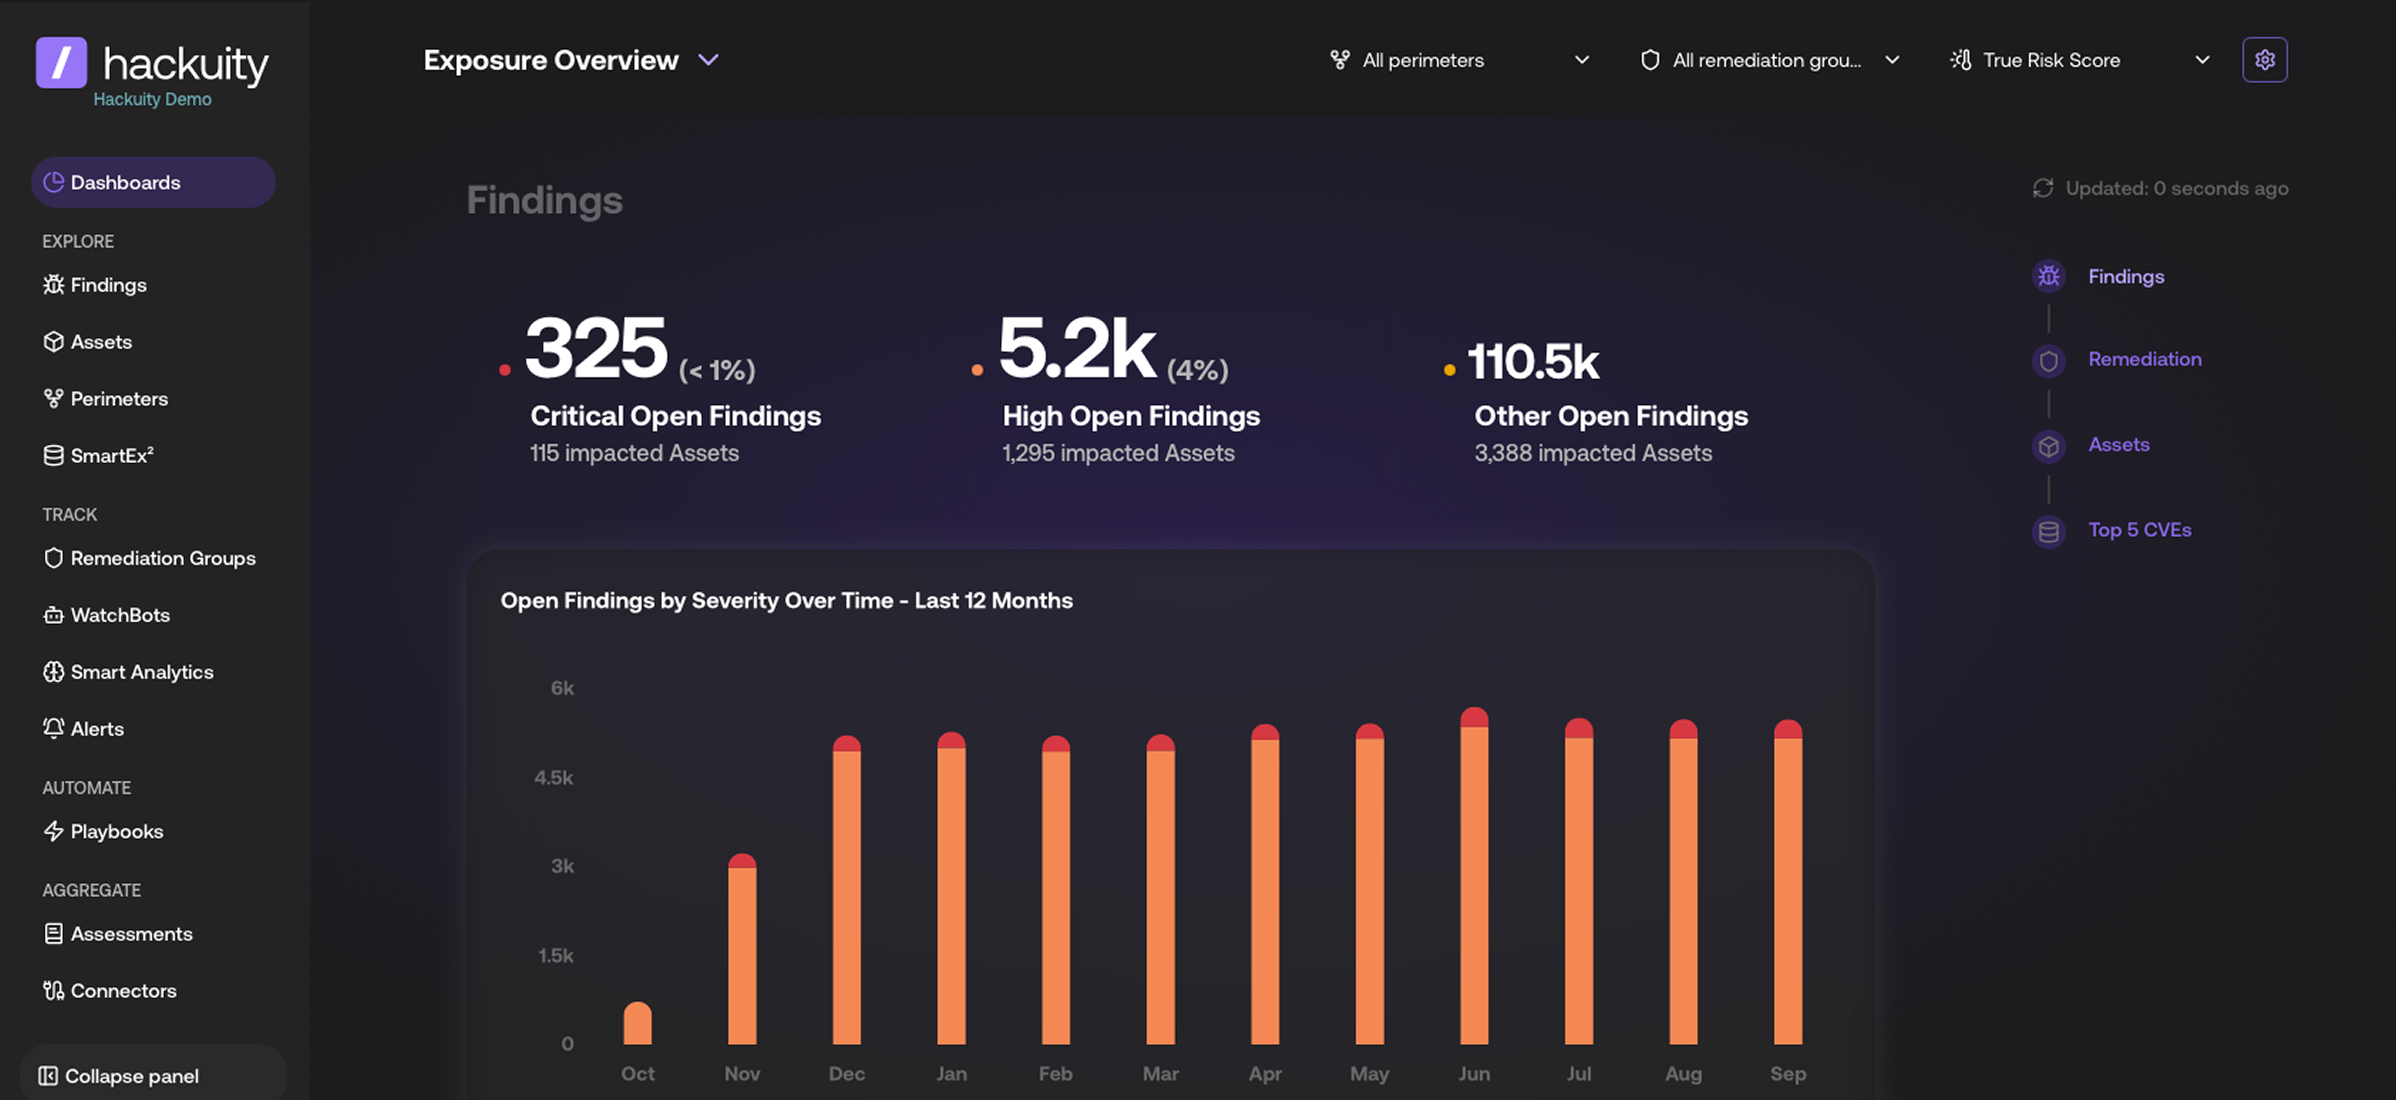
130+ connectors, continuous ingestion
No files: findings pulled automatically
ACE correlates and dedupes in real time
TRS: exploits, EPSS, KEV, asset context
Contextual tickets routed to ServiceNow / Jira...
Live SLA tracking, automatic escalation
NIS2 / DORA reports on demand

Why the manual workflow breaks

Every handoff needs a person. Each step waits for someone to export, merge, copy or send an email.

Context leaks between tools. Scores, owners and asset data get lost from one spreadsheet to the next, so IT receives tickets it can't act on.

Nobody sees the whole pipeline. Status lives in inboxes and Excel, so delays only surface at report time.

VS

Why it works with Hackuity

One pipeline, zero manual handoffs. Connectors feed ACE, which normalizes and deduplicates every finding as it arrives.

Context travels with the finding. TRS score, asset owner, SLA and remediation guidance land directly in the ticket.

Status is always live. SLAs and escalations run on their own, so reporting takes a click, not a day.

Automate the repetitive work. Keep humans in control.

Hackuity automates the steps that slow vulnerability management teams down, while keeping prioritization, remediation, and reporting explainable and measurable.
AUTOMATE AGGREGATION

Stop exporting. Start operating.

130+ native connectors pull findings from every scanner, cloud platform, and AppSec tool automatically. ACE, Hackuity's Aggregation, Correlation & Enrichment engine, normalizes, correlates, and deduplicates findings in real time. Your team starts each day with one clean, current pipeline, not four export files.
130+
native connectors into one exposure map
Explore VOC Framework
AUTOMATE TRIAGE

Let TRS do the scoring. Let your analysts do the thinking.
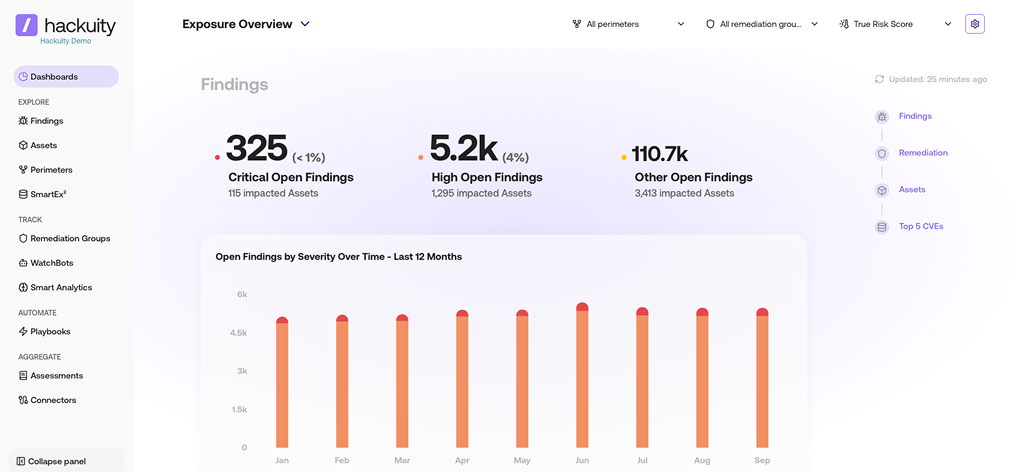
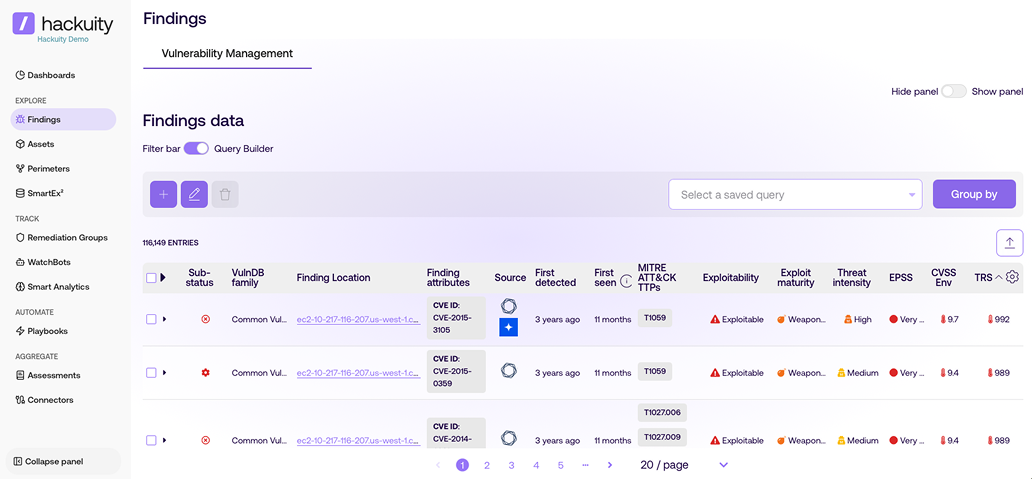
True Risk Score applies contextual risk scoring to every finding automatically, factoring exploit intelligence, EPSS, CISA KEV, and asset criticality. Your analysts inherit a prioritized queue, not a raw dump of CVEs.
÷38
critical findings on average after TRS
Explore RBVM Framework
AUTOMATE TICKET ROUTING

From finding to the right team, without human relay.
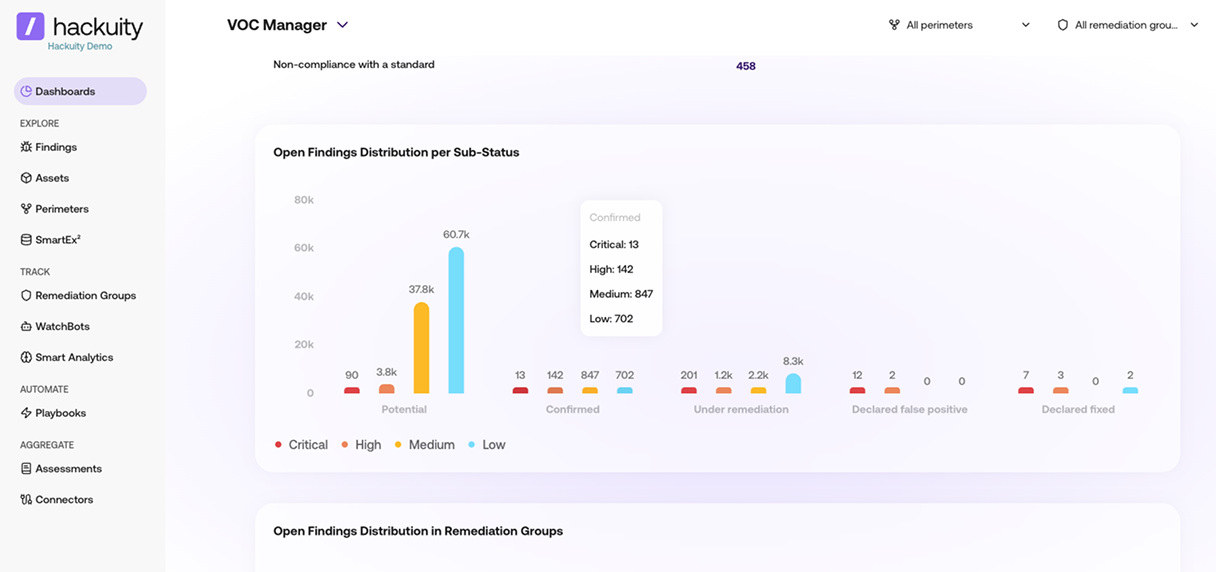
Hackuity connects directly to ServiceNow and Jira. Every prioritized finding generates a contextualized ITSM ticket with asset owner, TRS score, SLA deadline, and remediation guidance, then routes it automatically to the right team. IT receives tickets they can act on immediately.
x3
MTTR improvement, from finding to closed ticket.
Explore VOC Framework
AUTOMATE SLA TRACKING

Know what is on track, at risk, or breached, without asking.
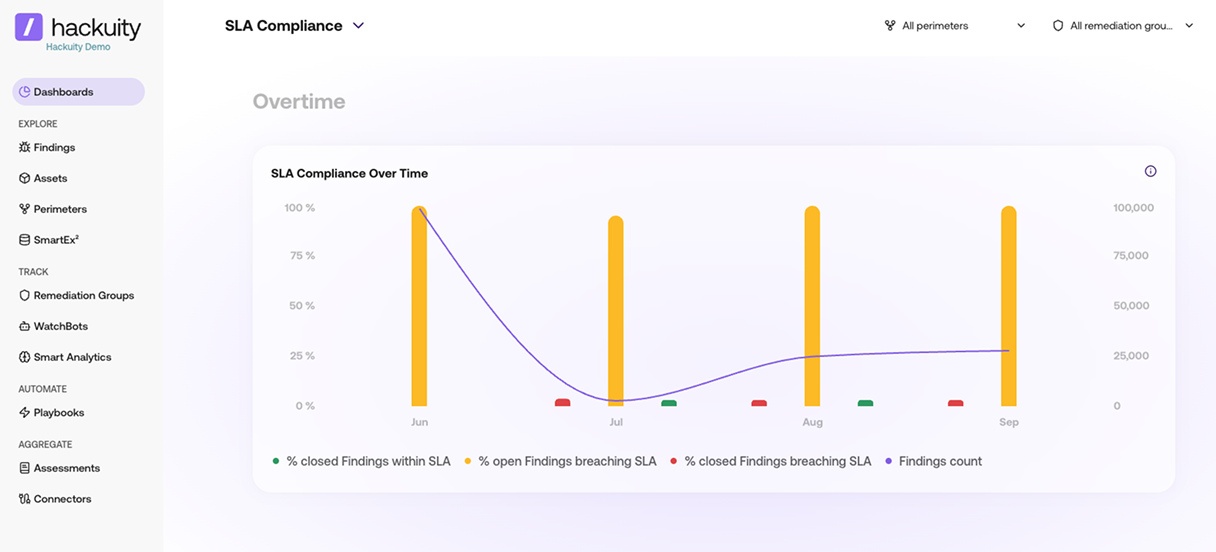
Every finding gets an SLA deadline on ingestion, based on risk level and your custom policy. A live dashboard shows the status of every finding across every team in real time. Escalations trigger automatically.
AUTOMATE REPORTING

Board-ready reports in minutes, not hours.
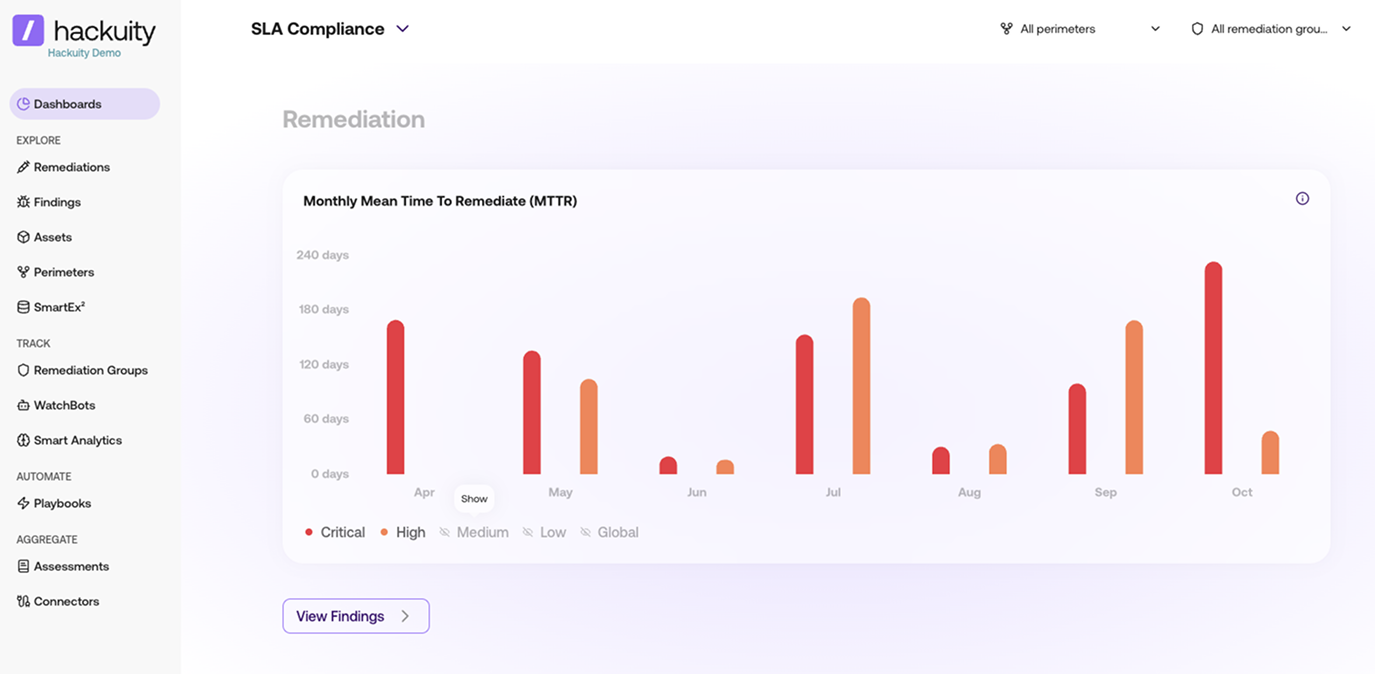
Risk posture dashboards, SLA compliance rates, MTTR trends, and regulatory coverage summaries for NIS2, DORA, and BOD 26-04 are generated on demand. Your CISO gets the data they need. Your team gets their time back.
PROOF

Measure how much time your team gets back.

70%
less manual work
Automate prioritization, remediation workflows, reporting, and ticket creation.
99.9%
Reduction in critical findings
Your team focuses on what matters most, not an endless backlog.
$3M
Saved per year
Savings across a 3-year VOC program.
x3
MTTR improvement
Less time chasing, more time closing.
130+
Connectors
No manual export, no normalization effort.

What efficiency looks like day to day.

PHASE
BEFORE HACKUITY
AFTER HACKUITY
Morning
Export from 4 tools, deduplicate manually.
1 unified queue, already prioritized by TRS
Triage
Manually score and qualify each finding.
TRS score and exploit context automatically and continuously applied.
Tickets
Create and route ITSM tickets one by one.
Auto-generated, contextualized, and routed.
Follow-up
Chase IT teams by email and in meetings.
SLA status visible per team, escalation automated.
Reporting
Build weekly status report manually.
Dashboard generated on demand.
End of day
Still behind.
Backlog is structured and shrinking.
AI-ASSISTED OPERATIONS

AI does the repetitive work.

As your program matures, Hackuity's AI agents take efficiency further by assisting with remediation planning, ticket creation, operational summaries, and compliance reporting.
Remediation Advisor
Answers operational questions in natural language. Generates morning briefs, compliance summaries, and SLA status on demand.
VOC Copilot
Answers operational questions in natural language. Generates morning briefs, compliance summaries, and SLA status on demand.

Continue building your exposure management program.

Vulnerability Operations Center

The operational model that makes efficiency possible.

Risk-Based Vulnerability Management

Prioritize contextually, not manually.

Agentic Remediation

AI-assisted patch prioritization and ticket automation.

MSSP

Scale efficient VM operations across multiple clients.

Trusted by leading enterprises

Before Hackuity, we were drowning in over 100,000 active alerts. Within three weeks, we contextualized our actual exposure and routed the critical 1% that mattered. It completely bridged the gap between our security and engineering teams.
Alex Mercer
CISO, Global Fintech Corporation
-98%
Critical findings reduced
3x
MTTR improved
94%
SLA compliance rate
80h
Manual reporting saved/mo

Recognized by leading authorities.
CyberSecAsia Awards 2026
Seal of Excellence
Wavestone
Forrester
IMDA Accreditation
CyberSecAsia Awards 2025
SOC 2 Type 2
EcoVadis Committed
CyberSecAsia Awards 2026
Seal of Excellence
Wavestone
Forrester
IMDA Accreditation
CyberSecAsia Awards 2025
SOC 2 Type 2
EcoVadis Committed
CyberSecAsia Awards 2026
Seal of Excellence
Wavestone
Forrester
IMDA Accreditation
CyberSecAsia Awards 2025
SOC 2 Type 2
EcoVadis Committed

Frequently asked questions

How does Hackuity help reduce exposure risk?

Hackuity automates aggregation, deduplication, risk prioritization, SLA assignment, ITSM routing, remediation tracking, and reporting, helping teams focus on the vulnerabilities that matter most.

Increase operational efficiency

Does Hackuity replace analysts?

No. Hackuity supports analysts by automating repetitive tasks while keeping human decision-making and oversight in place.

Increase operational efficiency

How does Hackuity reduce manual triage?

It consolidates findings, removes duplicates, adds business and threat context, and prioritizes the vulnerabilities requiring immediate attention.

Increase operational efficiency

How does Hackuity integrate with ITSM tools?

Hackuity integrates with tools such as ServiceNow, Jira, and Azure DevOps to create, route, and synchronize remediation tickets automatically.

Increase operational efficiency

Can Hackuity automate SLA tracking?

Yes. Hackuity assigns SLAs based on risk and asset criticality, then tracks progress, identifies breaches, and triggers escalations when needed.


Increase operational efficiency