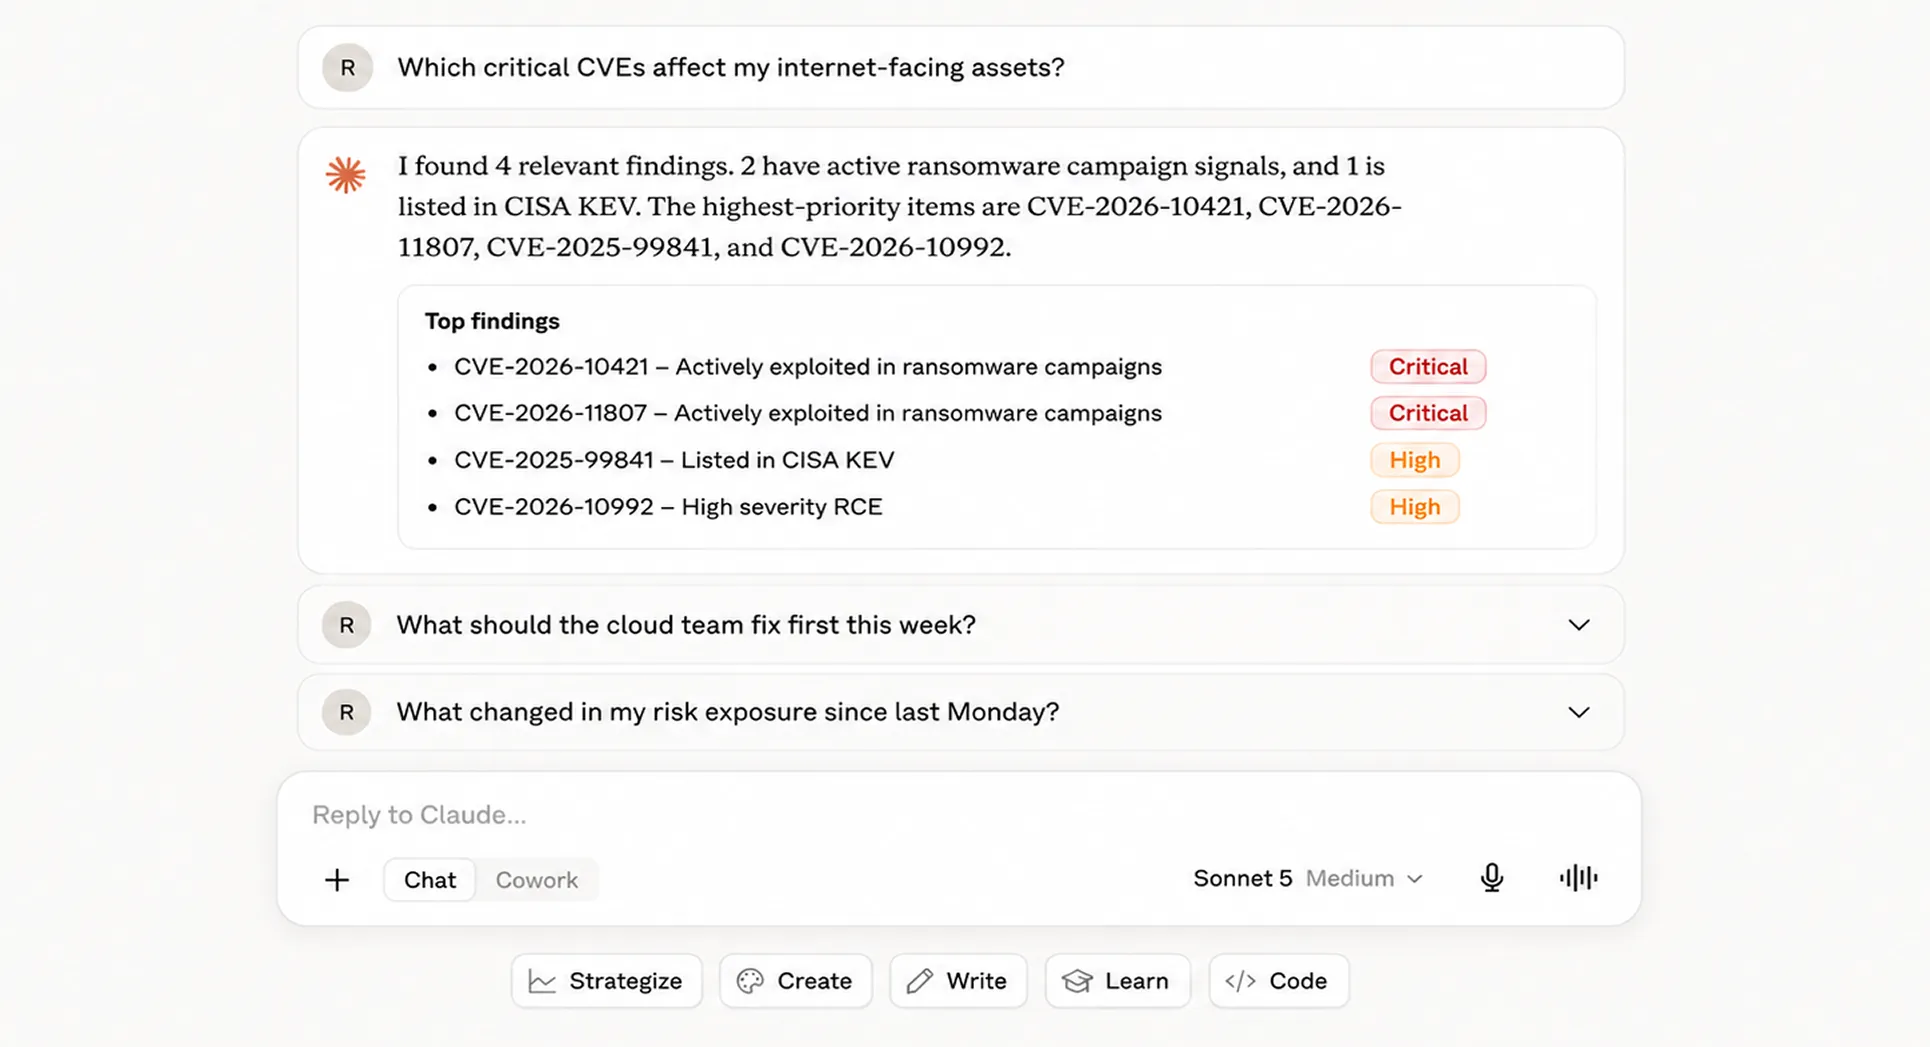
Bring vulnerability findings from every security tool into one platform. Prioritize what matters, coordinate remediation across teams, and reduce cyber risk faster.
Connect vulnerability scanners, cloud, appsec, IoT, ticketing ITSM, AD and more. No rip-and-replace required.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Popular integrations
Attack Surface Management
Recorded Future Attack Surface Intelligence
Recorded Future Attack Surface Intelligence is an external attack surface management solution that continuously discovers internet-facing assets, and identifies exposures and misconfigurations.
HTTPCS vulnerability scanner analyse and sort every URLs found on a website (or a web application) and theirs links to explore in priority the most relevant pages based on data partition algorithm, links analytics and language processing applied to URLs.
HTTPCS vulnerability scanner analyse and sort every URLs found on a website or a web application and theirs links to explore in priority the most relevant pages based on data partition algorithm, links analytics and language processing applied to URLs. Connect to the HTTPCS API and to seamlessly import and synchronize vulnerabilities within your Hackuity workspace.
Yogosha is an Offensive Security Testing Platform. Agilely launch and manage your security tests from end to end with this vulnerability management platform and its Strike Force of 800+ cybersecurity experts.
Yogosha is an Offensive Security Testing Platform. Agilely launch and manage your security tests from end to end with this vulnerability management platform and its Strike Force of 800+ cybersecurity experts. This integration allows users to retrieve VDP and Bug Bounty reports from Yogosha into your Hackuity platform.
Acunetix Premium is a web application security solution for managing the security of multiple websites, web applications, and APIs. Integration features allow you to automate your DevOps and issue management infrastructures.
IBM Security SOAR, formerly Resilient, is designed to help your security team respond to cyber-threats with confidence, automate with intelligence, and collaborate with consistency.
IBM Security® QRadar® SOAR, formerly Resilient®, is designed to help your security team respond to cyberthreats with confidence, automate with intelligence and collaborate with consistency. It guides IT team in resolving incidents by codifying established incident response processes into dynamic playbooks. It is a bi-directional connector that allows full integration of IBM Security QRadar SOAR processes into Hackuity.
HelixALM is a modular suite of ALM tools. You can use this application lifecycle management (ALM) suite to trace requirements, tests, and issues. HelixALM provides end-to-end traceability across the application lifecycle. This plugin allows to create and follow HelixALM issues (change requests, feature requests, ...) from Hackuity workplace.
Hadrian is an External Attack Surface Management (EASM) platform that provides agentless external attack surface monitoring with comprehensive asset discovery and vulnerability scanning capabilities.
This connector integrates Hadrian's externally scanned assets (domains and IPs) with their risks into Hackuity [Arriving in imminent release | 1 month +].
HackerOne is a security platform that connects businesses with a community of ethical hackers to proactively identify and fix security vulnerabilities. It allows organizations to launch bug bounty programs to reward security researchers who discover and report security flaws.