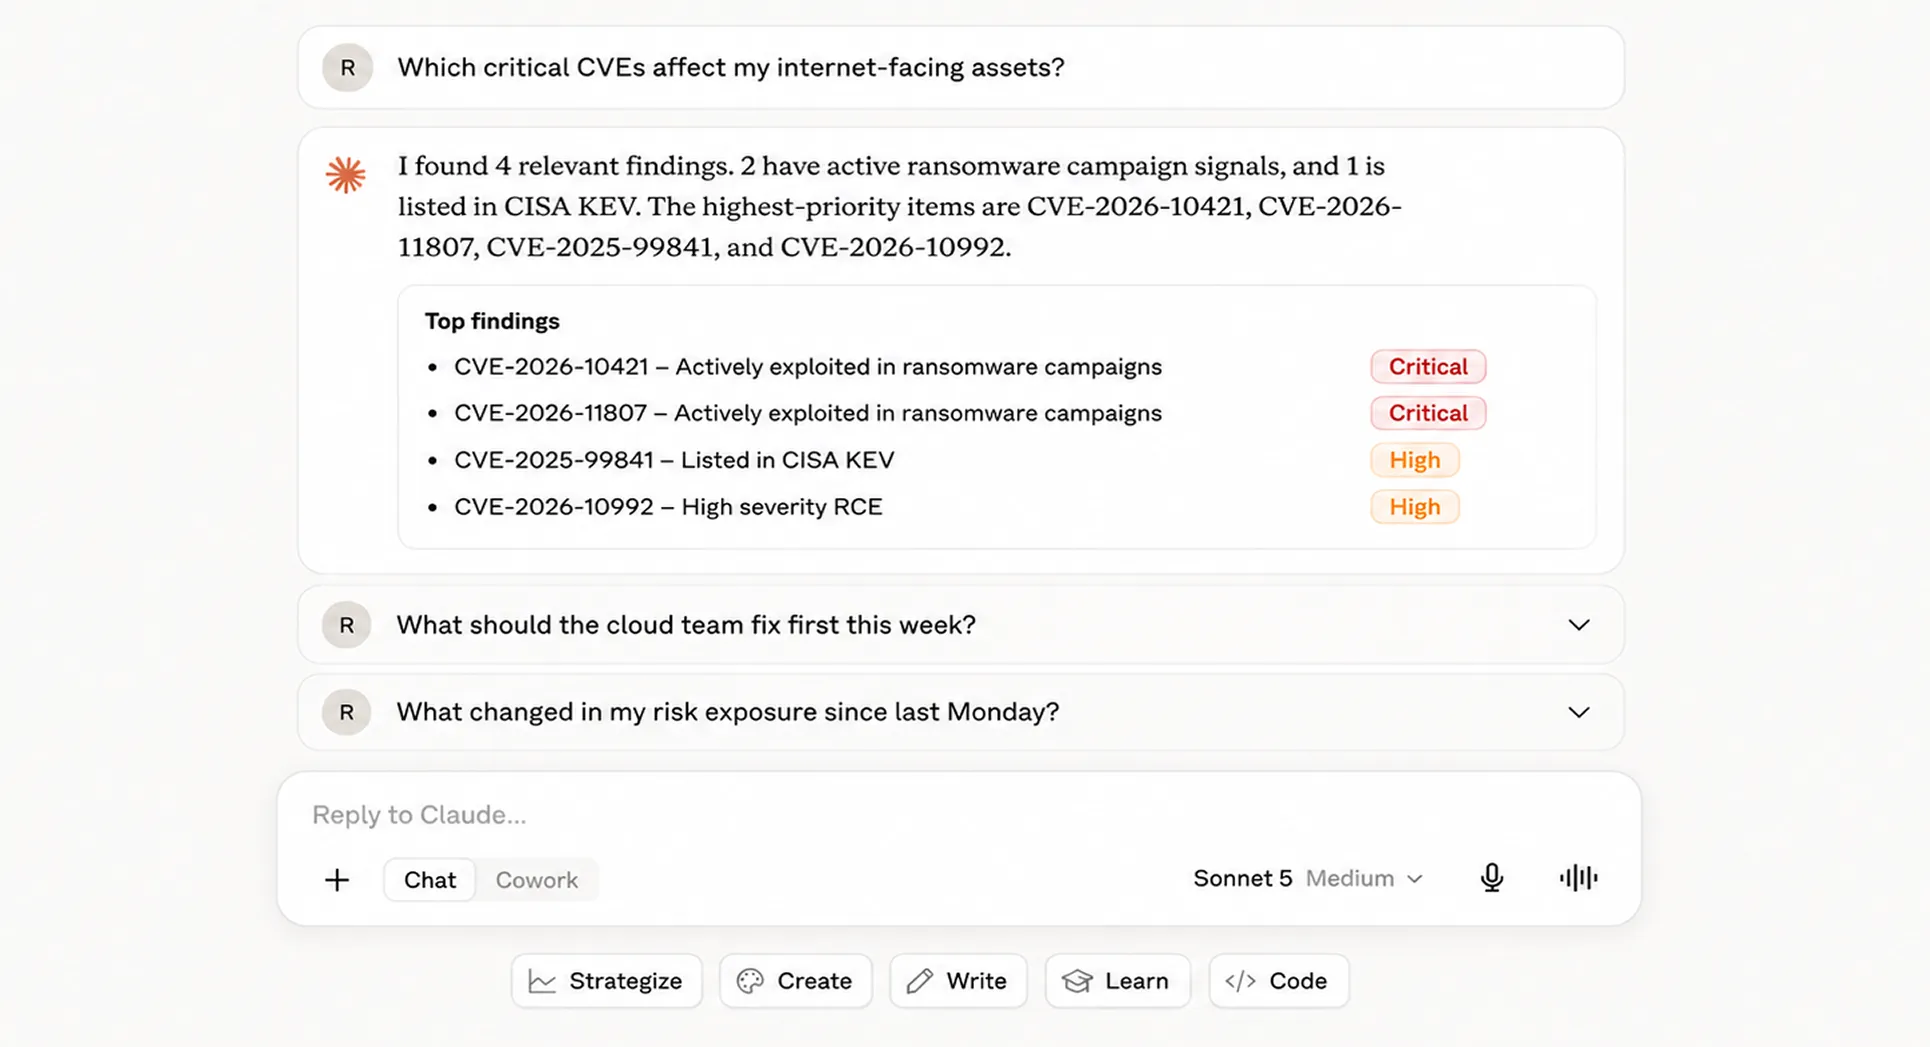
Bring vulnerability findings from every security tool into one platform. Prioritize what matters, coordinate remediation across teams, and reduce cyber risk faster.
Connect vulnerability scanners, cloud, appsec, IoT, ticketing ITSM, AD and more. No rip-and-replace required.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Popular integrations
Pentest as a service
Ambionics Security
By using an offensive attacker’s point of view, Ambionics has created an efficient and realistic approach which oversteps the limits of classical manual or automated assessment. Through the combination of its powerful technical platform and its team of experts in breach tactics, Ambionics provides to companies an innovative solution for continuous web application security assessment.
By using an offensive attacker’s point of view, Ambionics has created an efficient and realistic approach which oversteps the limits of classical manual or automated assessment. Through the combination of its powerful technical platform and its team of experts in breach tactics, Ambionics provides to companies an innovative solution for continuous web application security assessment.
ORADAD helps dumping Active Directory data via LDAP to assist security audit assignments. It has been designed to be easier to use and extend than DirectoryCrawler. It also supports multi-domain forests.
ORADAD connector allows to import results of Active Directory security auditing into Hackuity Platform. Findings are turned on ANSSI security standards with a set of compliances rules associated to AD Forest, AD Domain and AD objects like accounts.
In order to improve the security of the Internet in France, the ANSSI, the national authority for the security of information systems, regularly performs network scans. The purpose of these network scans is to reduce the number of devices that can be exploited by attackers.
The ANSSI provides regulated operators and the public sphere with a mapping capability of their exposure surface on the Internet through the SILENE service. This service aims to give visibility to these operators on their level of exposure and to accompany them by the progressive application of adequate measures to reduce it. The ANSSI SILENE connector allows users to seamlessly import a .ZIP file and synchronize ANSSI SILENE reports within your Hackuity workspace.
OpenVAS is a full-featured vulnerability scanner. Its capabilities include unauthenticated and authenticated testing, various high-level and low-level internet and industrial protocols, performance tuning for large-scale scans and a powerful internal programming language to implement any type of vulnerability test. The scanner obtains the tests for detecting vulnerabilities from a feed that has a long history and daily updates. Import a OpenVAS scan by uploading a XML OpenVAS output in the Hackuity workplace to create a vulnerability assessment mapped with the OpenVAS information.
HackerOne is a security platform that connects businesses with a community of ethical hackers to proactively identify and fix security vulnerabilities. It allows organizations to launch bug bounty programs to reward security researchers who discover and report security flaws.
Hadrian is an External Attack Surface Management (EASM) platform that provides agentless external attack surface monitoring with comprehensive asset discovery and vulnerability scanning capabilities.
This connector integrates Hadrian's externally scanned assets (domains and IPs) with their risks into Hackuity [Arriving in imminent release | 1 month +].
HarfangLab Hurukai is an endpoint detection and response platform. Its vulnerability management module inventories the software installed on every managed endpoint and reports the CVEs affecting it.
Import every managed endpoint as an asset including the endpoints carrying no vulnerability and the CVEs currently active on them as findings, each with the software of that endpoint the CVE affects.
HelixALM is a modular suite of ALM tools. You can use this application lifecycle management (ALM) suite to trace requirements, tests, and issues. HelixALM provides end-to-end traceability across the application lifecycle. This plugin allows to create and follow HelixALM issues (change requests, feature requests, ...) from Hackuity workplace.
IBM Security SOAR, formerly Resilient, is designed to help your security team respond to cyber-threats with confidence, automate with intelligence, and collaborate with consistency.
IBM Security® QRadar® SOAR, formerly Resilient®, is designed to help your security team respond to cyberthreats with confidence, automate with intelligence and collaborate with consistency. It guides IT team in resolving incidents by codifying established incident response processes into dynamic playbooks. It is a bi-directional connector that allows full integration of IBM Security QRadar SOAR processes into Hackuity.