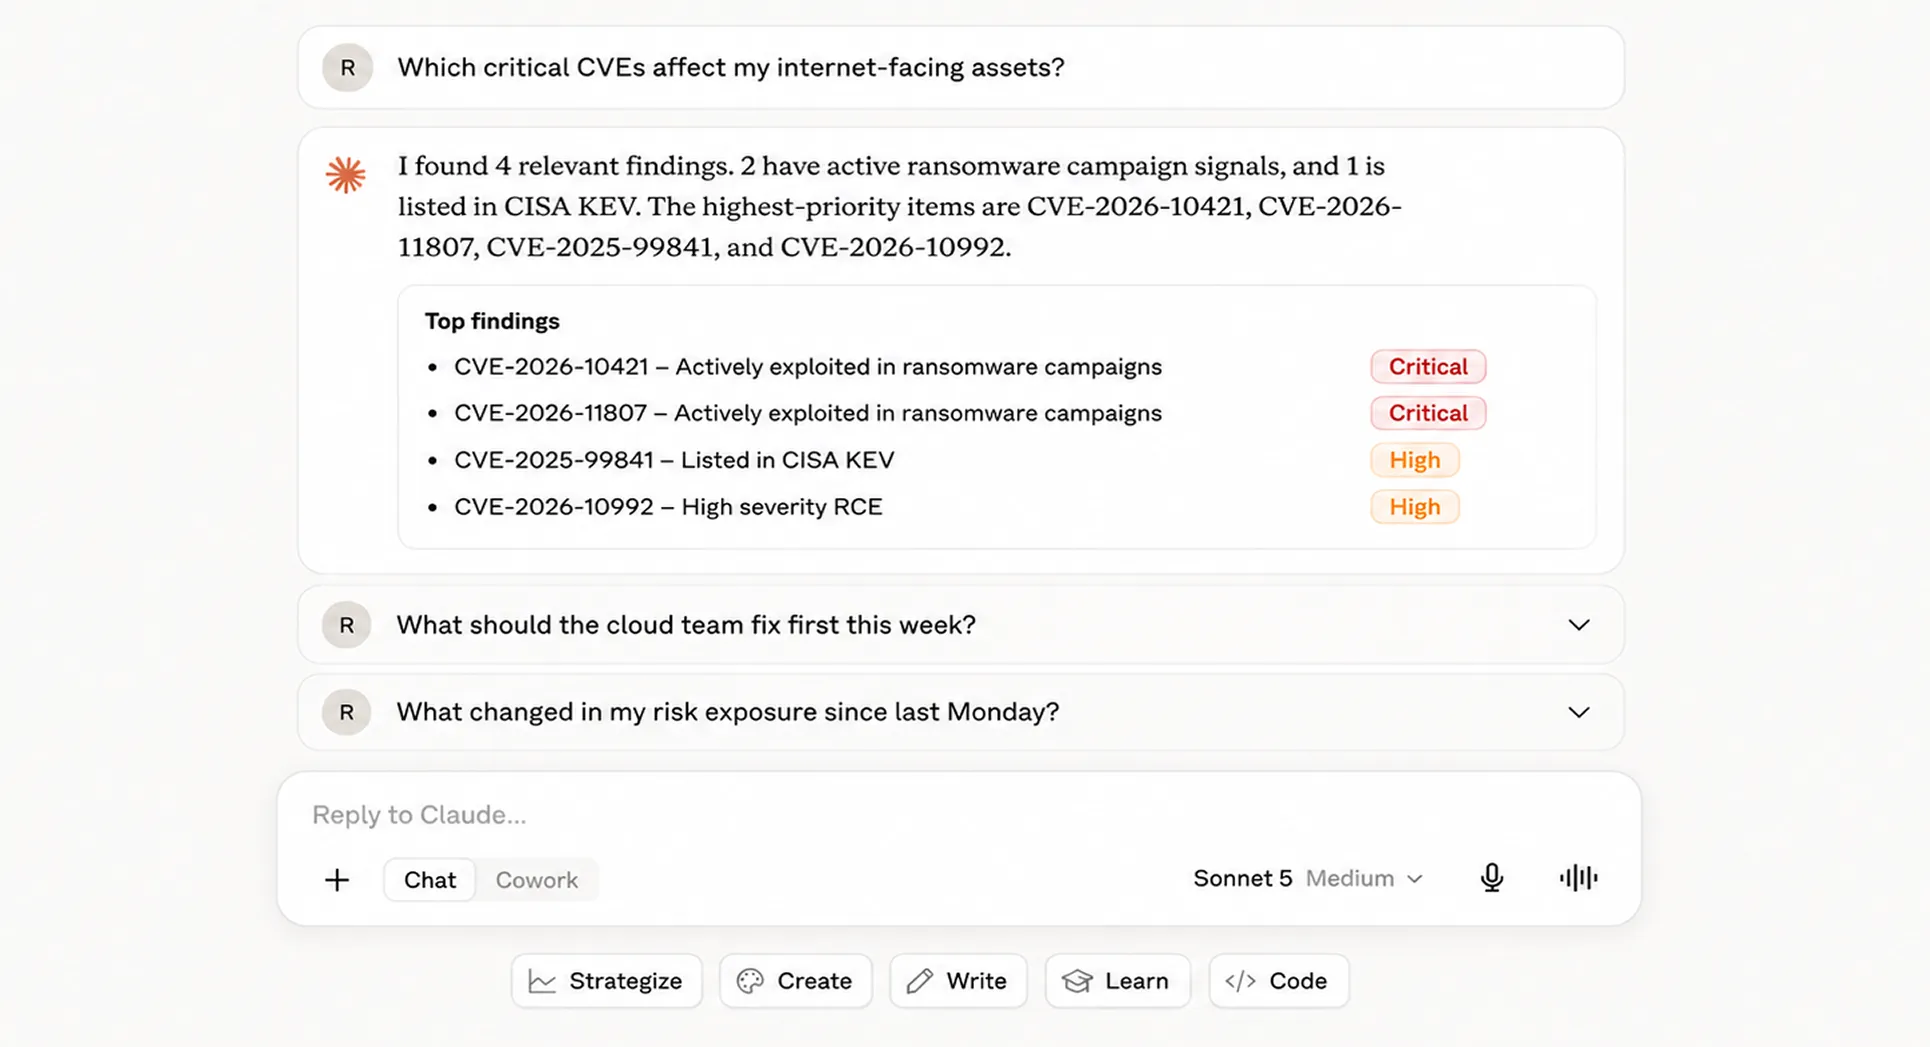
Bring vulnerability findings from every security tool into one platform. Prioritize what matters, coordinate remediation across teams, and reduce cyber risk faster.
Connect vulnerability scanners, cloud, appsec, IoT, ticketing ITSM, AD and more. No rip-and-replace required.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Popular integrations
Attack Surface Management
Recorded Future Attack Surface Intelligence
Recorded Future Attack Surface Intelligence is an external attack surface management solution that continuously discovers internet-facing assets, and identifies exposures and misconfigurations.
HTTPCS vulnerability scanner analyse and sort every URLs found on a website (or a web application) and theirs links to explore in priority the most relevant pages based on data partition algorithm, links analytics and language processing applied to URLs.
HTTPCS vulnerability scanner analyse and sort every URLs found on a website or a web application and theirs links to explore in priority the most relevant pages based on data partition algorithm, links analytics and language processing applied to URLs. Connect to the HTTPCS API and to seamlessly import and synchronize vulnerabilities within your Hackuity workspace.
Yogosha is an Offensive Security Testing Platform. Agilely launch and manage your security tests from end to end with this vulnerability management platform and its Strike Force of 800+ cybersecurity experts.
Yogosha is an Offensive Security Testing Platform. Agilely launch and manage your security tests from end to end with this vulnerability management platform and its Strike Force of 800+ cybersecurity experts. This integration allows users to retrieve VDP and Bug Bounty reports from Yogosha into your Hackuity platform.
Qualys WAS gives you visibility and control by finding official and “unofficial” apps throughout your environment, and letting you categorize them. Connect to the Qualys WAS API to seamlessly import, de-duplicate, normalize, and prioritize vulnerabilities within your Hackuity work environment.
Qualys VMDR is a cloud-based service that gives global visibility into where IT systems might be vulnerable to the latest Internet threats and how to protect them. Connect to the Qualys VM API to seamlessly import, de-duplicate, normalize, and prioritize vulnerabilities within your Hackuity work environment.
Qualys Security Configuration Assessment (SCA) evaluates system configurations against industry benchmarks and policies, helping organizations identify, report, and remediate misconfigurations across on‑premises and cloud environments.
Connect to Qualys SCA to import and synchronize configuration Findings and Assets into Hackuity for centralized compliance analysis and prioritization.
Qualys Enterprise TruRisk Management (ETM) is a cloud-based platform that aggregates assets and security findings from Qualys and third-party tools to centralize, prioritize, and orchestrate cyber risk management.
Qualys Enterprise TruRisk Management (ETM) aggregates cyber risk signals across Qualys and third‑party tools to measure, prioritize, and orchestrate remediation with business context and unified risk scoring.
Connect to Qualys ETM to import and synchronize Assets, Vulnerabilities, and Findings into Hackuity for centralized analysis and prioritization. [Arriving in imminent release | 1 month +].
Qualys CyberSecurity Asset Management (CSAM) helps you to identify all systems comprehensively, detect at-risk assets, and respond with appropriate actions to mitigate risk.
Continuously detect and track web application technology changes with real-time alerts on new vulnerabilities, new technologies, new versions, and revised ratings.
Purplemet is a Web Application Security monitoring platform to follow the web security exposure over time. Connect to the Purplemet API to seamlessly import, de-duplicate, normalize, and prioritize vulnerabilities within your Hackuity work environment.
The Most Complete Cloud-Native Application Protection Platform (CNAPP).
Prisma Cloud secures applications from code to cloud, enabling security and DevOps teams to effectively collaborate to accelerate secure cloud-native application development and deployment.
Prisma Cloud CSPM from Palo Alto Networks continuously monitors cloud configurations and compliance across AWS, Azure, and Google Cloud, detecting misconfigurations and policy violations to reduce risk in multicloud environments.
Connect to Prisma Cloud CSPM to import and synchronize cloud Assets and Findings into Hackuity for centralized analysis, compliance tracking, and prioritization.