Connect your stack. Prioritize from one place.

Bring vulnerability findings from every security tool into one platform. Prioritize what matters, coordinate remediation across teams, and reduce cyber risk faster.

Works with the security tools you already use

Connect vulnerability scanners, cloud, appsec, IoT, ticketing ITSM, AD and more.
No rip-and-replace required.
INTEGRATIONS TYPES
All
Showing
0
of
137
connectors
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

Popular integrations

Attack Surface Management
Recorded Future Attack Surface Intelligence
Recorded Future Attack Surface Intelligence is an external attack surface management solution that continuously discovers internet-facing assets, and identifies exposures and misconfigurations.
Connector Details
Active
Recorded Future Attack Surface Intelligence
API connection
Attack Surface Management
What can I do with it?
Connect to Recorded Future Attack Surface Intelligence to import and synchronize discovered Assets and Findings into Hackuity.
Application security
Ziwit HTTPCS
HTTPCS vulnerability scanner analyse and sort every URLs found on a website (or a web application) and theirs links to explore in priority the most relevant pages based on data partition algorithm, links analytics and language processing applied to URLs.
Connector Details
Active
Ziwit HTTPCS
API connection
Application security
What can I do with it?
HTTPCS vulnerability scanner analyse and sort every URLs found on a website or a web application and theirs links to explore in priority the most relevant pages based on data partition algorithm, links analytics and language processing applied to URLs. Connect to the HTTPCS API and to seamlessly import and synchronize vulnerabilities within your Hackuity workspace.
Bug bounty
Yogosha
Yogosha is an Offensive Security Testing Platform. Agilely launch and manage your security tests from end to end with this vulnerability management platform and its Strike Force of 800+ cybersecurity experts.
Connector Details
Active
Yogosha
API connection
Bug bounty
What can I do with it?
Yogosha is an Offensive Security Testing Platform. Agilely launch and manage your security tests from end to end with this vulnerability management platform and its Strike Force of 800+ cybersecurity experts. This integration allows users to retrieve VDP and Bug Bounty reports from Yogosha into your Hackuity platform.
Integrations catalogue
Endpoint security
Pradeo
Pradeo secures corporate mobile device fleets and supports the development and protection of mobile applications.
Connector Details
Active
Pradeo
API connection
Endpoint security
What can I do with it?
Pradeo connector allows you to import your mobile device fleet and their non-compliances against your response policies into Hackuity.
Data analytics
PowerBI
Power BI is a Business Intelligence (BI) solution developed by Microsoft, enabling users to consolidate, analyze, visualize and distribute their Hackuity data.
Connector Details
Active
PowerBI
File upload
Data analytics
What can I do with it?
The integration consists of an off-the-shelf PowerBI project, which enables deep data analytics and reporting on your vulnerability stock.
Active Directory Security
PingCastle
PingCastle launches a series of AD requests (LDAP or AD webservice) to check a set of best practices and configurations.
Connector Details
Active
PingCastle
API connection
Active Directory Security
What can I do with it?
The integration enables PingCastle to receive information linked to the analysis of active directories in Hackuity. [Arriving in imminent release | 1 month +]
Attack Surface Management
Patrowl
Patrowl automates the detection and remediation of assets (shadow-IT) and vulnerabilities with pentest automation.
Connector Details
Active
Patrowl
API connection
Attack Surface Management
What can I do with it?
This connector import and synchronize assets, qualified vulnerabilities and risks insights from Patrowl API into your Hackuity environment.
Asset inventory
Attack Surface Management
PaloAlto Cortex Xpanse
PaloAlto Cortex Xpanse is an attack surface management platform that collects and correlates active and passive information about every device and service connected to the public Internet.
Connector Details
Active
PaloAlto Cortex Xpanse
API connection
Asset inventory
Attack Surface Management
What can I do with it?
Connect to the PaloAlto Cortex Xpanse to seamlessly import and synchronize vulnerabilities data within your Hackuity platform.
Endpoint security
PaloAlto Cortex XDR
Cortex XDR delivers enterprise-wide protection by analyzing data from any source to stop sophisticated attacks.
Connector Details
Active
PaloAlto Cortex XDR
API connection
Endpoint security
What can I do with it?
Connect to the PaloAlto Cortex XDR API to seamlessly import and synchronize vulnerabilities identified on your endpoints within your Hackuity platform.
Collaboration tools
Palo Alto Cortex XSOAR
Cortex™ XSOAR is a comprehensive security orchestration, automation and response (SOAR) platform that unifies case management, automation, real-time collaboration and threat intel management to serve security teams across the incident lifecycle. This connector needs to be setup in the Palo Alto Cortex XSOAR interface. From a war-room, query your Hackuity cockpit in order to seamlessly retrieve information related to your vulnerability stock. This integration was integrated and tested with version 1.25.0 of Hackuity.

Connector Details
Active
Palo Alto Cortex XSOAR
API connection
Collaboration tools
What can I do with it?
Cortex™ XSOAR is a comprehensive security orchestration, automation and response (SOAR) platform that unifies case management, automation, real-time collaboration and threat intel management to serve security teams across the incident lifecycle. This connector needs to be setup in the Palo Alto Cortex XSOAR interface. From a war-room, query your Hackuity cockpit in order to seamlessly retrieve information related to your vulnerability stock. This integration was integrated and tested with version 1.25.0 of Hackuity.
Application security
OWASP Dependency-Check
The OWASP® Foundation works to improve the security of software through its community-led open source software projects, hundreds of chapters worldwide, tens of thousands of members, and by hosting local and global conferences.
Connector Details
Active
OWASP Dependency-Check
File upload
Application security
What can I do with it?
The OWASP® Dependency-Check is a Software Composition Analysis (SCA) tool that attempts to detect publicly disclosed vulnerabilities contained within a project’s dependencies. It does this by determining if there is a Common Platform Enumeration (CPE) identifier for a given dependency. If found, it will generate a report linking to the associated CVE entries. OWASP® Dependency-Check import permits to create assessments by uploading a .json file to your Hackuity workplace.
Infrastructure scanner
Outpost 24 NetSec
Outpost24 offers all the tools, insights and data you need to uncover security risk exposure across your entire attack surface.
Connector Details
Active
Outpost 24 NetSec
API connection
Infrastructure scanner
What can I do with it?
Outpost24 offers all the tools, insights and data you need to uncover security risk exposure across your entire attack surface.
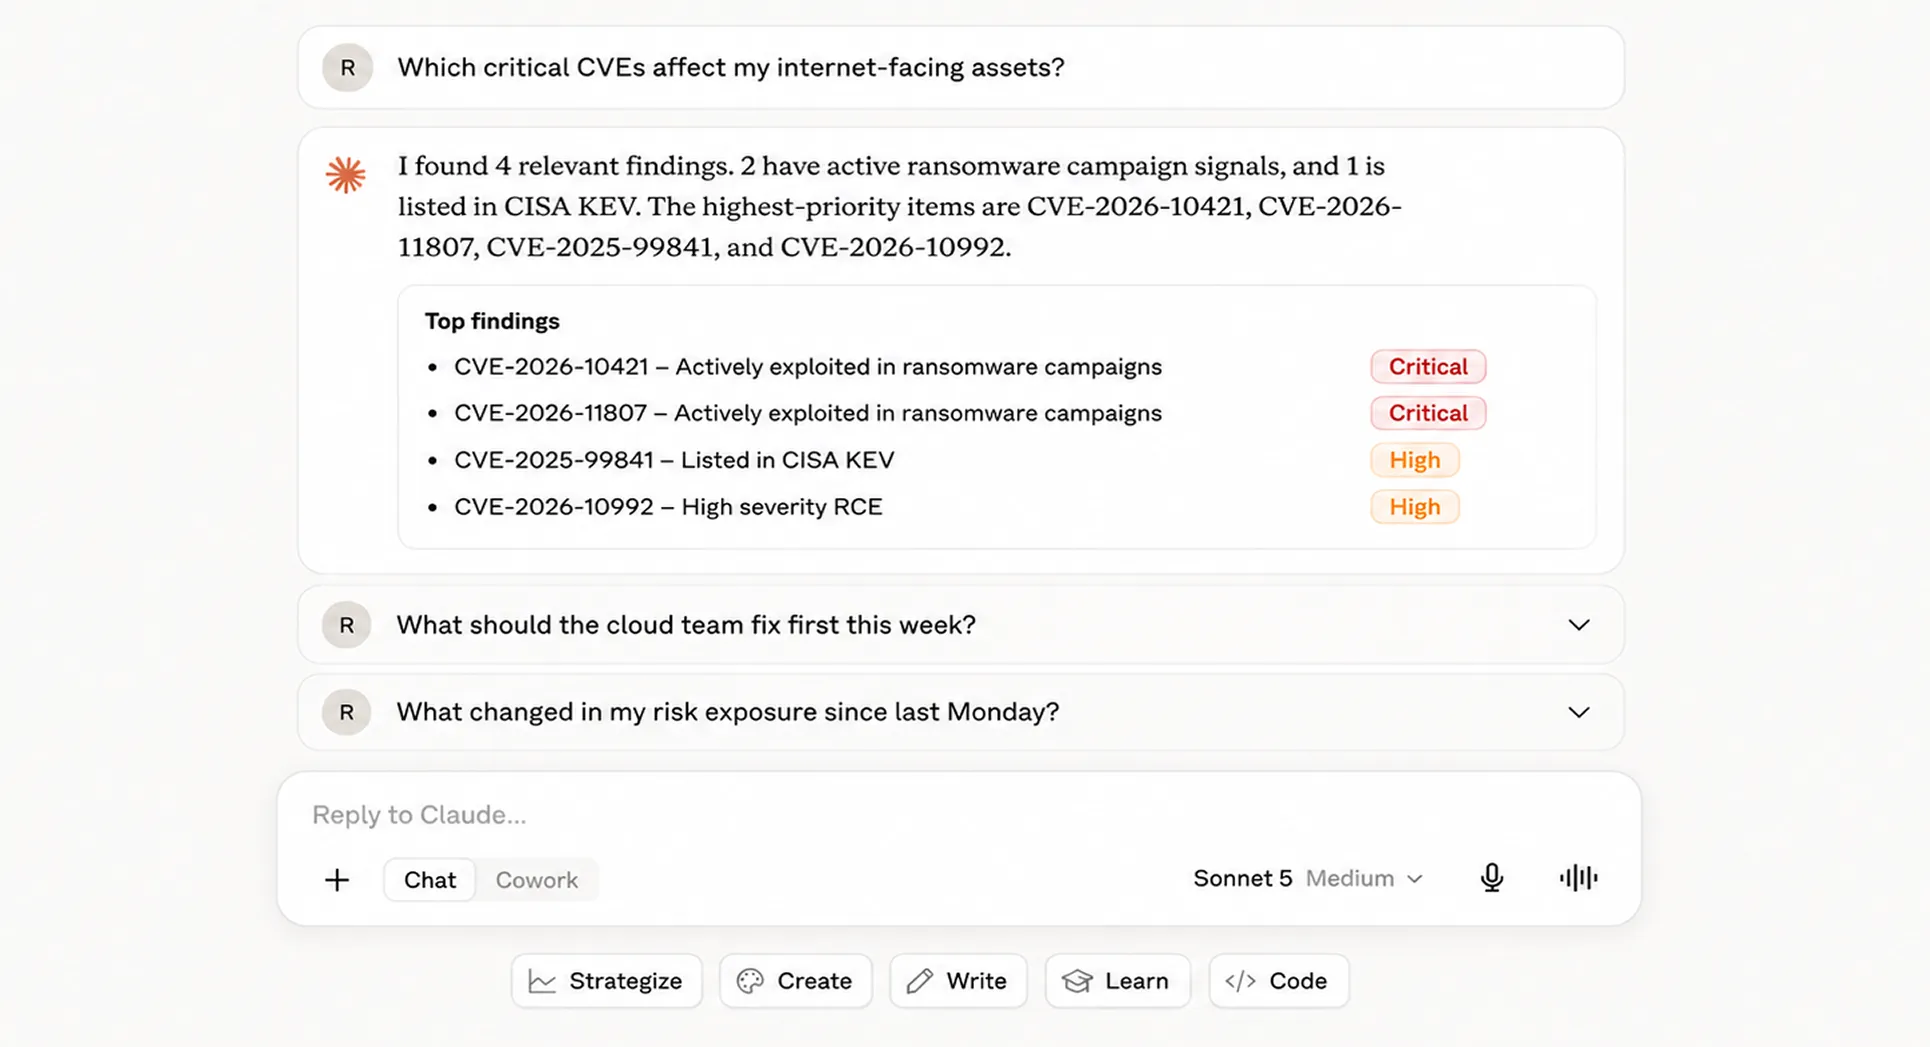
AGENTIC AI

Your AI agents speak Hackuity, natively.

Connect vulnerability scanners, cloud, appsec, IoT, ticketing ITSM, AD & more.
No rip-and-replace required.
Hakuity MCp server is Compatible with

Don't see your tool?

We can usually connect it quickly through our APIs or build a custom integration. Tell us what you use, and we’ll help you get connected.