Faster vulnerability discovery will not reduce risk unless organizations can prioritize, assign, remediate, and prove what actually gets fixed.
The question raised by Anthropic's June 9 announcement is no longer whether AI can accelerate vulnerability discovery. It increasingly can. The harder problem is whether organizations can prioritize, assign, remediate, and prove risk reduction at the same speed. This announcement makes that gap more urgent, not because it introduces a new threat, but because it brings Mythos-class capability closer to everyday software delivery.
What Anthropic Actually Announced
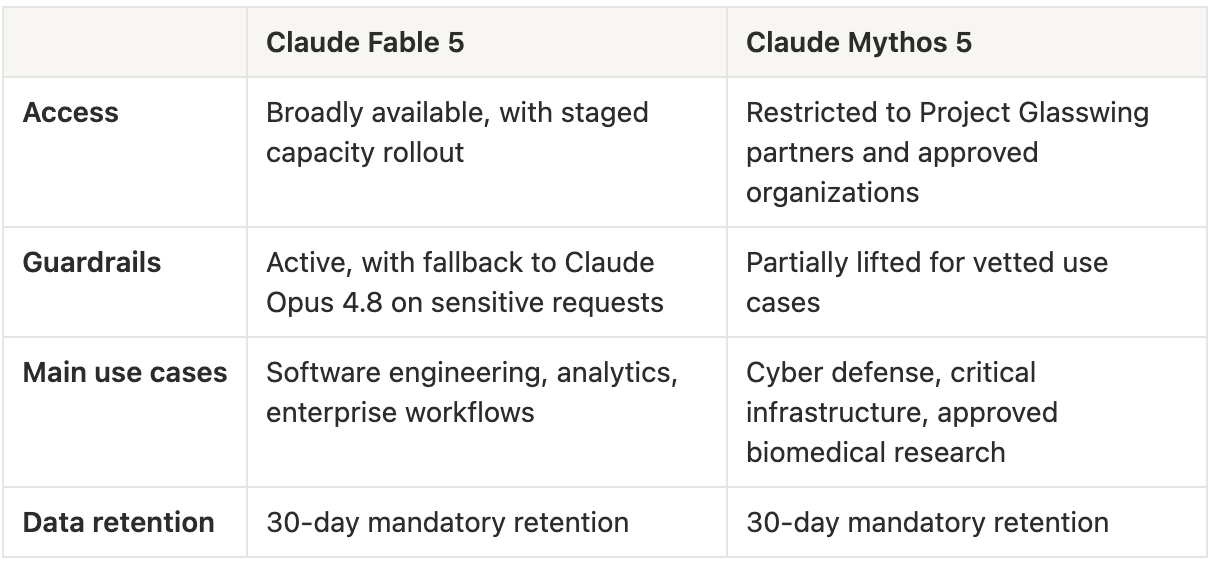
Fable 5 and Mythos 5 are not two entirely separate model families. They are built on the same underlying model, exposed through two access levels.
Anthropic lists both models at the same API price: $10 per million input tokens and $50 per million output tokens.¹
When Fable 5 detects certain sensitive requests touching cybersecurity, biology, chemistry, or model distillation, it automatically routes the session to Claude Opus 4.8. Anthropic says this fallback affects fewer than 5% of sessions.¹ In sessions without fallback, Fable 5 performs at effectively the same level as Mythos 5. Mythos 5, meanwhile, remains restricted to vetted defenders and selected high-trust use cases through Project Glasswing.²
This is not a small-model versus large-model distinction. It is a trust-tiered access model: the same frontier capability, exposed through different governance layers depending on who is asking and what for. That architecture may become a template for how frontier AI capabilities are deployed in high-risk domains.
Why Security Teams Should Care
Code will move faster. Risk will follow.
Anthropic reports that Fable 5 completed a codebase-wide migration across a 50-million-line Ruby codebase in a single day a task estimated at two months for a skilled team.¹ Faster code delivery also means faster dependency changes, faster configuration drift, and faster propagation of insecure patterns across repositories. The vulnerability workload does not shrink because developers become more productive. If anything, the surface area security teams must reason about expands, while most security organizations are unlikely to scale at the same rate as the code and environments they are expected to protect.
AI is moving deeper into triage.
Previous models could assist analysts with point queries. Fable 5 can support more autonomous multi-step workflows, analyzing a codebase, reasoning across components, recovering from partial failures with less constant human steering. That moves AI from a tool answering isolated prompts to an agent participating more directly in triage and analysis workflows. That is a meaningful shift for how security operations may be structured.'
Access to less-restricted AI now matters.
Anthropic reports improved performance on controlled cyber evaluations, including ExploitBench and CyberGym³ though those benchmarks should be treated as capability indicators rather than operational guarantees. The point is not the specific scores. It is that access to advanced AI capability is becoming differentiated, and that differentiation may shape how vulnerability analysis work gets done in practice.
The Backlog Problem AI Won't Solve Alone
If AI increases both the volume and the speed of vulnerability discovery through more capable scanning, agentic code analysis, and faster development tooling, security teams will face a new form of backlog inflation: more findings, more suggested remediations, more contextual signals, but not proportionally more remediation capacity.
The unit of work for a security team is not a finding. It is a validated exposure with an owner, a priority, a deadline, and a remediation path.
In a risk-based vulnerability management program, the value of AI is not to surface more vulnerabilities. It is to connect vulnerability data with exploitability signals, asset criticality, exposure context, and remediation ownership so that the output of AI-assisted discovery translates into prioritized, executable action rather than an expanding list of things that technically need attention. Without that framework, more powerful AI becomes a more efficient way to generate noise.
Without Governance, AI Just Adds Noise
Anthropic built a governance system around Fable 5 and Mythos 5: capability gating, sensitive-use classifiers, mandatory data retention, and differentiated trusted access.¹ These design choices reflect a deliberate answer to the question of who should be able to do what, under what controls, and with what traceability.
Security organizations deploying Mythos-class models in their own workflows will need to answer the same question clearly. Three things should be defined before any deployment in a real vulnerability management context:
- Who can invoke these models, on what data, and under what authorization?
- Where does human validation enter the workflow and where can it not be skipped?
- How do AI-generated findings become traceable remediation decisions?
AI can recommend. Platforms must contextualize. Humans must decide. Workflows must track execution. Any deployment that skips one of those steps risks becoming a faster way to generate unactionable output.
What Matters Is What Gets Fixed
Anthropic is pointing toward a future where Mythos-class capabilities become more accessible through controlled trust programs, rather than remaining locked away. Fable 5 is already moving into enterprise development channels. Mythos 5 is expanding to vetted defenders.²
But controlled access is only one part of the story. As advanced AI capabilities diffuse, the real question for security leaders will not be whether these systems can surface more vulnerabilities. They will. The question is whether organizations can turn that intelligence into fewer, better-prioritized, actually remediated exposures before attackers can act on similar AI-generated signals.
That question becomes even sharper if comparable capabilities emerge through open-weight models with weaker safeguards, weaker access controls, or no equivalent governance layer at all. In that scenario, the advantage will not belong to the organizations that generate the most findings. It will belong to the ones that can validate, prioritize, assign, remediate, and prove risk reduction the fastest.
That is the problem Hackuity is built to solve.


VR-1 | Property |
|---|---|
Model type | Post-trained cyber reasoning model |
Primary specialization | Multi-domain enterprise attack-chain discovery |
Starting condition | A scoped foothold and a concrete objective |
Operating surfaces | Cloud, identity, runtime, code, CI/CD, SaaS, and organizational context |
Success signal | Execution-verified completion of the objective |
Primary evaluation | IntrusionBench |
Preliminary result (preview) | More than 2× black-box pass@3 over the strongest evaluated frontier baseline |
Trajectory budget | Two-hour wall-clock limit per trajectory, or 250 agent turns (whichever comes first) |