





















Article
Blog
Insights, research, and practical guidance to help security teams prioritize risk, accelerate remediation, and stay ahead of modern threats.
Most recent
Article
Expert View
5 minutes
read
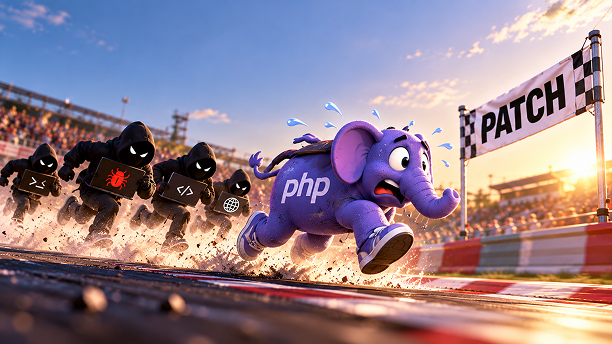
PHP2Shell: The Patch Was Scheduled. The PoC Came First.
Two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, were patched on October 21. Thirteen and a half hours earlier, an independent researcher had already published a reconstruction of them, apparently built from a handful of public clues.
October 21, 2026
Library
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Article
Expert View
8 min
read
From Risk to Decisions: Why SSVC Is the Missing Piece
You've got better severity scores. You've got risk context. Now you need to actually decide what to do. This is the final piece of the puzzle. In our first article, we covered how CVSS v4 improved severity measurement. In the second, we explored how TRS adds threat and environmental context to calculate actual risk. But even with accurate severity and comprehensive risk scoring, most vulnerability management programs stall at the same point: turning data into consistent decisions. Your team knows which vulnerabilities are risky. But how do you consistently decide what gets fixed this week versus next month? How do you explain those choices when engineering teams push back? SSVC (Stakeholder-Specific Vulnerability Categorization) solves this. It turns your risk signals into defensible, repeatable decisions.
August 25, 2026
Article
Hackuity in the News
5 min
read
From noise to action – how context transforms vulnerability management?
I see many organizations fall into the “patch everything now” trap, treating any delay as a ticking time bomb. Ironically, this constant sense of urgency can make for a less efficient patch management process. Chasing every CVE as...
August 25, 2026
Article
Hackuity in the News
3 min
read
Experts welcome EU-led alternative to MITRE's vulnerability tracking scheme
The EU-led framework will reduce reliance on US-based MITRE vulnerability reporting database.Cybersecurity experts have welcomed the launch of the new Global CVE Allocation System (GCVE) as a positive move toward more robust vulnerability..

August 25, 2026
Article
Expert View
5 min
read
CVSS v4, Two Years On: What The Data Really Say
When CVSS v4 launched in November 2023, the security community had questions. Would organizations actually adopt it? Would the refined scoring methodology deliver on its promises? And most importantly, would it help security teams make better decisions? Two years in, we finally have answers. And they're not what everyone expected.
August 25, 2026
Article
Expert View
8 min
read
CVSS Is Necessary, But Not Sufficient. Here's Why.
You've got a “Critical” CVSS score. Now what? In the article about CVSSv4 adoption, we saw that CVSS gives you a number. That number tells you the vulnerability is severe. It doesn't tell you whether attackers are actively exploiting it. It doesn't tell you if it's on an internet-facing server or an isolated dev box. It doesn't tell you if you have detection coverage or strong compensating controls. That gap between severity and risk is where security teams get stuck. CVSS v4 brought improvements to severity scoring, with adoption accelerating faster than expected and more accurate base scores. But even with those improvements, CVSS wasn't designed to answer the operational question: what do I fix first? That's the problem Hackuity's True Risk Score (TRS) solves.
August 25, 2026
Article
Hackuity in the News
4 min
read
Building A Rapid-Response Vulnerability Operation
The window of time for dealing with security vulnerabilities is shrinking. Research has found that, of 432 distinct CVEs exploited in the wild during the first half of 2025, nearly a third (32%) were abused on or before the day...
August 25, 2026



