













Article
Blog
Insights, research, and practical guidance to help security teams prioritize risk, accelerate remediation, and stay ahead of modern threats.
Most recent
Hackuity in the News
5 minutes
read
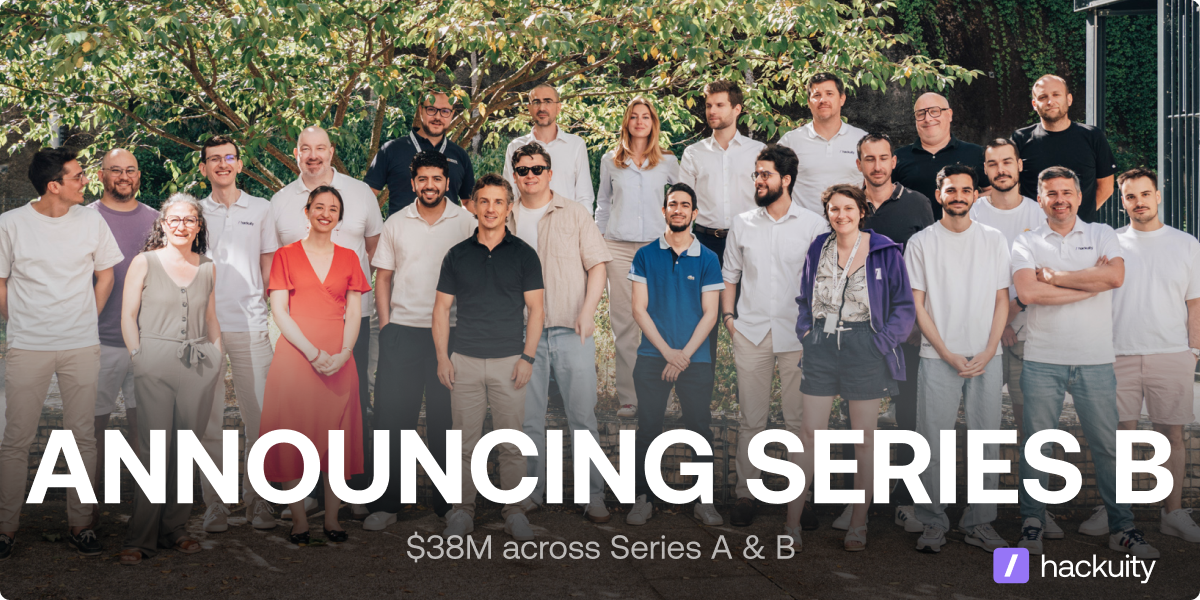
Hackuity raises $19M Series B to scale the AI-powered Vulnerability Operations Center
Today we announced $19 million in new funding, bringing Hackuity's total funding to $38 million. The round was led by Forgepoint Capital International, alongside our existing investors Bright Pixel, Bpifrance and Seventure Partners.
September 16, 2026
Library
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Article
Expert View
10 min
read
Navigating the Cisco Vulnerability Management End of Life: A Strategic Inflection Point for Security Programs
On December 9, 2025, Cisco issued an official end-of-life announcement that changes the landscape for many security teams: Cisco Vulnerability Management, Vulnerability Intelligence, and Application Security Module (formerly Kenna) will reach end-of-support on June 30, 2028. The announcement includes a critical detail that elevates this from a routine technology refresh to a strategic decision point: Cisco has explicitly stated there is no replacement available for these products at this time. This is not a migration to a next-generation Cisco platform. It is a complete exit from this market segment, requiring customers to reassess their vulnerability management approach.The timeline provides approximately 42 months from announcement to final support cutoff. Sales end March 10, 2026. Service renewals stop June 11, 2026. After mid-2028, organizations still running Cisco Vulnerability Management will operate without vendor support, security updates, or technical assistance. 💡Here is the good news: if your organization has been running Kenna successfully, you already have something more valuable than any platform—you have the operational foundation in place to transition smoothly and evolve further.
August 25, 2026
Article
Hackuity in the News
4 min
read
More code, more flaws: scaling vulnerability management for the AI era
Software is being built at record speed, but security is falling behind. In fact, recent research found that 81% of organisations knowingly shipped vulnerable code last year to meet the pressure for shorter production lifecycles.
August 25, 2026
Article
Hackuity in the News
5 min
read
Looking ahead to 2026 with Sylvian Cortes, Hackuity
As part of an online miniseries, Sylvian Cortes, Vice President of Strategy at Hackuity discusses his industry predictions for 2026. Can you tell me a bit about yourself, your job role and how long you have been at the company?

August 25, 2026
Article
Hackuity in the News
5 minutes
read
Ineffective Vulnerability Management Is A Hidden Business Risk
In this Q&A, Sylvain Cortes, VP Strategy at Hackuity, discusses why ineffective vulnerability management is becoming a hidden business risk – and how organisations can realign it with business priorities.
August 25, 2026
Article
Expert View
8 min
read
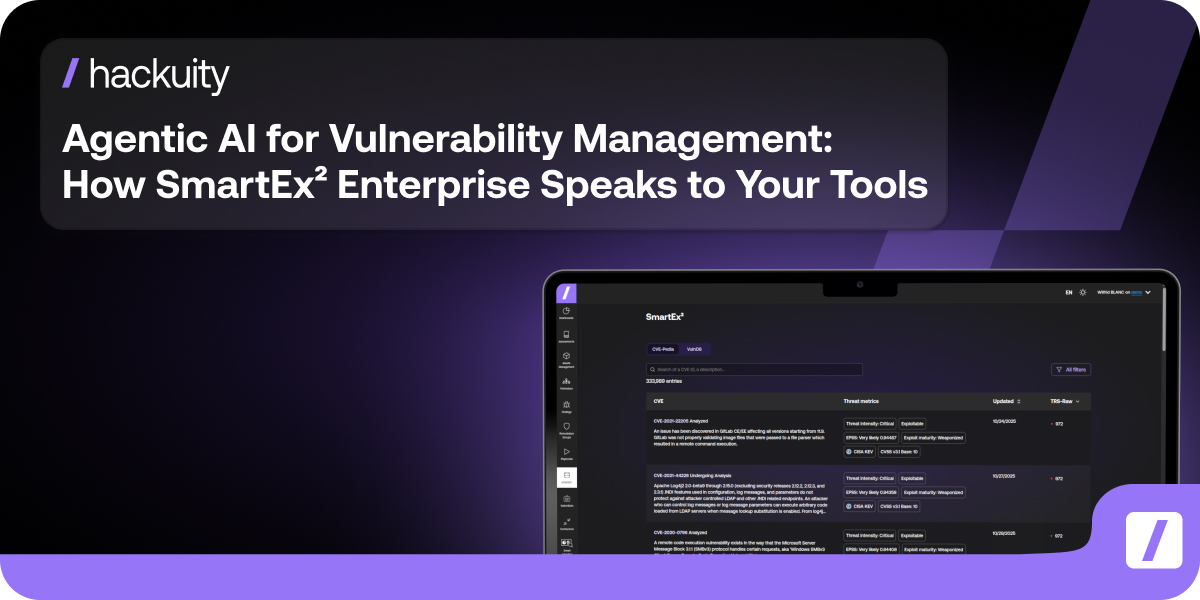
Agentic AI for Vulnerability Management: How SmartEx² Enterprise Speaks to Your Tools
You're not short on vulnerability & exploit data. You're short on time to make sense of it all. Every morning, your team faces the same challenge: dozen of new CVEs, tens marked "critical," some actually exploited in the wild. Which ones threaten YOUR environment? Which ones can wait? You need answers fast, but getting them means querying multiple sources, correlating threat intelligence, and connecting dots manually. What if your security tools could answer these questions themselves? That's what agentic AI makes possible. Instead of you querying data, AI agents continuously monitor, analyze, and surface the intelligence you need. Autonomously.
August 25, 2026



